





Detailed explanation of Slashing economics in Pos protocol
Original title: "The cryptoeconomics of slashing》
Original Author: Sreeram Kannan, Soubhik Deb
Compilation of the original text: Overnight Porridge
Compilation of the original text: Overnight Porridge
Of the mechanisms designed for Proof of Stake (PoS) protocols, none is as controversial as Slashing. Slashing provides a way to financially penalize any specific node for not acting in a protocol-consistent manner in a targeted manner. It does this by taking away some or all of validator stake, without imposing externalities on other nodes behaving in accordance with the protocol. Slashing is unique to Proof of Stake (PoS) protocols because it requires the blockchain to be able to enforce penalties. This kind of enforcement is obviously not feasible in a proof-of-work (PoW) system, which is similar to burning the mining hardware used by misbehaving nodes. This ability to apply punitive incentives opens up a new design space in blockchain mechanism design and thus deserves careful consideration.
While it brings obvious benefits in the form of "karma", the main objection to slashing is that nodes can be excessively slashed due to inadvertent mistakes such as running outdated software. As a result, many protocols avoid slashing and instead rely on so-called token toxicity (i.e., if the protocol is successfully attacked, the underlying token loses value). Many believe that stakers will view this toxicity as a threat to compromising the security of the protocol. In our evaluation, token toxicity is not sufficient to prevent adversarial attacks in some typical scenarios. In fact, in this case, the cost incurred by the adversary to attack and break the protocol (called the bribe cost) is essentially zero.
In this paper, we show how slashing (slashing) can be incorporated into the mechanism design of PoS protocols, thereby greatly increasing the cost of bribery that any adversary can incur. In the presence of bribery, slashing guarantees high and measurable bribery costs for decentralized protocols as well as for protocols that do not satisfy token toxicity assumptions (centralized or decentralized).
Circumstances that could lead to bribery and lack of token toxicity are ubiquitous. Many PoS protocols avoid falling into either of these two categories by having a tight-knit community, which is only feasible when they are small. (1) Delegate validation to a small set of well-known and legally regulated node operators by relying on strong leadership to steer them in the right direction; (2) or rely on centralizing staked tokens within a small group. None of these solutions are entirely satisfactory for growing large and decentralized validator communities. If the PoS protocol is characterized by only a few validators (or, in extreme cases, only one validator), then it would be nice to have a way to penalize these large validators for engaging in adversarial behavior.
In the remainder of this article, we:
Propose a model to analyze complex bribing attacks;
Shows that PoS protocols without a slashing mechanism are vulnerable to bribery attacks;
Show that the PoS protocol with slashing mechanism has quantifiable security against bribery attacks;
As well as discussing some of the disadvantages of slashing and suggesting mitigations.
1. Model
Before introducing the forfeiture case, we first need a model under which we will conduct our analysis. The two most popular models currently analyzing PoS protocols (Byzantine models and game-theoretic equilibrium models) fail to capture some of the most damaging real-world attacks against which slashing acts as a powerful deterrent. In this section, we discuss these existing models to understand their shortcomings and propose a third model (which we call the bribery analysis model). Although the bribing analysis model is capable of simulating a large number of attacks, it has not been used to analyze many protocols.
existing model
In this section, we briefly describe Byzantine and game-theoretic equilibrium models and their shortcomings.
Byzantine model
For example, consider the longest-chain PoS consensus protocol, where liveness takes precedence over safety. Early research on the security of longest-chain consensus focused on demonstrating security against a specific attack (i.e., a private double-spend attack, in which all Byzantine nodes secretly collude to build an alternate chain and then to make it public). However, the nothing-at-stake phenomenon presents an opportunity to propose many blocks with the same stake, and use independent randomness to increase the likelihood of building longer private chains. Extensive research was not done until much later to show that certain structures of the longest-chain PoS consensus protocol are resistant to all attacks against certain values of 𝜷. (For more details, see theEverything is a Race and Nakamoto Always Wins"as well as"PoSAT: Proof-of-Work Availability and Unpredictability, Without the Work》)
"as well as"HotStuff: BFT Consensus in the Lens of Blockchain》、《STREAMLET》、《Tendermint》。)
An entire class of Byzantine Fault Tolerant (BFT) consensus protocols that prioritize safety over liveness. They also need to assume a Byzantine model to prove that, for an upper bound on 𝜷, these protocols are deterministically secure against any attack. (For more details, see the
As useful as the Byzantine model is, it does not take into account any economic incentives. From a behavioral point of view, 𝜷 part of these nodes is completely adversarial in nature, while (1-𝜷) part of nodes fully conforms to the protocol specification. In contrast, a large proportion of nodes in a PoS protocol may be motivated by economic gain and run a modified version of the protocol that benefits its own interests, rather than simply adhering to the full protocol specification. To give a prominent example, consider the case of the Ethereum PoS protocol. Today, most nodes do not run the default PoS protocol, but run the MEV-Boost modified protocol. This is because participating in the MEV auction market will generate additional rewards, while running The exact canonical protocol does not have this additional bonus.
Game Theoretic Equilibrium Model
Game-theoretic equilibrium models attempt to address the shortcomings of the Byzantine model by using solution concepts such as the Nash equilibrium to study whether rational nodes have an economic incentive to follow a given strategy when all other nodes also follow the same strategy. More specifically, assuming everyone is rational, the model investigates two questions:
If all other nodes follow the protocol-mandated policy, is it in my best economic interest to enforce the same protocol-mandated policy?
If every other node is enforcing the same policy of deviating from the protocol, is it most incentivized for me to still follow the policy?
Ideally, the protocol should be designed so that the answer to both questions is "yes".
An inherent shortcoming of the game-theoretic equilibrium model is that it excludes scenarios where exogenous agents may affect the behavior of nodes. For example, external agents can set bribes to incentivize rational nodes to behave according to their stated policies. Another limitation is that it assumes that each node has an independent agency that can decide for itself which strategy to adopt, based on its ideology or economic incentives. But that doesn’t cover scenarios where a group of nodes colludes to form a cartel, or where economies of scale encourage the creation of a centralized entity that essentially controls all staking nodes.
Separating bribery costs from bribery profits
Some researchers proposed a bribery analysis model to analyze the security of any PoS protocol, although no one used it for a deeper analysis. The model begins by asking two questions: (1) What is the minimum cost required for any adversary to successfully perform a security or liveness attack on the protocol? (2) What is the maximum profit an adversary can gain from successfully executing a protocol security or liveness attack?
And the opponent in question might be:
Nodes that unilaterally deviate from the policy stipulated in the agreement;
A group of nodes actively cooperating with each other to break the protocol, or
External adversaries who try to influence the decisions of many nodes through external actions such as bribery.
Calculating the costs involved takes into account any costs incurred for bribery, any financial penalties for enforcing a Byzantine strategy, etc. Likewise, calculating profit is all-encompassing, including in-protocol rewards from successful attacks on the protocol, any value captured from DApps sitting on top of PoS protocols, holding protocol-related derivatives on secondary markets, and Profit from incoming volatility, and so on.
Comparing the lower bound on the minimum cost for any adversary to launch an attack (bribe cost) with the upper bound on the maximum profit the adversary can extract (bribe profit) shows that the attacking protocol is economically profitable (note: the model has been used to analyze Augur and Kleros), which gives us a simple equation:
Bribe Profit – Bribe Cost = Total Profit
If the total profit is positive, then the adversary has an incentive to attack. In the next section, we consider how slashing can increase the cost of bribes and reduce or eliminate total profits. (Note that a simple example of a cap on bribing profits is the total value of assets secured by a PoS protocol. More complex bounds can be established, taking into account circuit breakers that limit asset transfers over time. Details of methods for reducing and capping bribing profits research, is beyond the scope of this article.)
2. Slashing
Slashing is a way for PoS protocols to economically penalize a node or group of nodes for implementing a strategy that is provably different from a given protocol specification. Typically, to implement any form of slashing, each node must have previously committed a certain amount of stake as collateral. Before diving into slashing, we will first examine PoS systems with native tokens that rely on token toxicity as an alternative to slashing.
We mainly focus on the study of slashing mechanisms for security violations, not liveness violations. We propose this limitation for two reasons: (1) security violations are fully attributable to some BFT-based PoS protocols, but liveness violations are not attributable to any protocol, and (2) security violations are usually more severe than liveness violations, This results in a loss of user funds, not the user's inability to post transactions.
Is there any problem if there is no penalty?
Consider a PoS protocol consisting of N rational nodes (no Byzantine or altruistic nodes). Let us assume, for computational simplicity, that each node deposits an equal amount of stake. We first explore how token toxicity does not warrant significant bribery costs. For consistency throughout the document, we also assume that the PoS protocol used is a BFT protocol with ⅓ adversary threshold.
Token toxicity is not enough
A common view is that token toxicity protects staking protocols from any attack on their security. Token toxicity implies the fact that if the protocol is successfully attacked, the underlying tokens used to stake in the protocol will lose value, thereby inhibiting participating nodes from attacking the protocol. Consider the scenario of 1/3 stakers teaming up: these nodes can cooperate to break the security of the protocol. But the question is can it be done with impunity?
If the total valuation of staked tokens is strictly dependent on the security of the protocol, then any attack on the security of the protocol could reduce its total valuation to zero. Of course, in practice it doesn't drop directly to zero, but to some smaller value. But in order to show the strongest possible case of token toxicity, we will assume here that token toxicity works perfectly. The bribery cost of any attack on the protocol is the tokens held by rational nodes attacking the system, and they must be willing to lose all of this value.
We now analyze the incentives for collusion and bribery in token-toxic PoS systems without slashing. Assume that the external opponent sets the bribery conditions as follows:
If the node follows the strategy indicated by the opponent but the attack on the protocol is unsuccessful, the node receives a reward B 1 from the opponent.
If the node follows the strategy indicated by the opponent and the attack on the protocol is successful, the node receives a reward B 2 from the opponent.

For the nodes depositing the stake S, we can get the following income matrix, and R is the reward for participating in the PoS protocol:Suppose the adversary sets the bribe payoff as B 1>R and B 2>0 . In this case, no matter what strategy other nodes adopt (the dominant strategy), the rewards of accepting a bribe from an opponent are higher than any other strategy the node can adopt. If 1/3 of the other nodes end up accepting the bribe, they can attack the security of the protocol (this is because we assume we are using a BFT protocol with an adversary threshold of ⅓). Now, even if the current node does not take the bribe, the token loses its value anyway due to token toxicity (top right cell in the matrix). Therefore, it is incentive compatible for nodes to accept B2 bribes. If only a small percentage of nodes accept the bribe, the token does not lose value, but the nodes benefit from forgoing the reward R and gaining B 1 instead (left column in the matrix). If 1/3 of the nodes agree to accept bribes and the attack is successful, then the total cost of bribes paid by the opponent is at least 𝑁/3 × B 2 , which is the cost of bribes. However, the only condition for B2 is that it must be greater than zero, therefore, B2 can be set close to zero, which means that the cost of bribery is negligible. This attack is called。
"P+ε" attack
One way of summarizing this effect is that token toxicity is not enough, because the impact of bad behavior is social: token toxicity completely devalues the value of the token, affecting both good and bad nodes equally. On the other hand, the benefits of taking bribes are privatized and limited to those rational nodes that actually take bribes. There are no one-to-one consequences for those who take bribes, that is, there is no working version of "karma" in this system.
Does token toxicity always work?
Another misleading claim that is popular in the ecosystem is that every PoS protocol has some degree of protection through token toxicity. But in fact, the exogenous incentives of token toxicity do not extend to certain classes of protocols where the valuation of tokens used as pledged face value does not depend on the safe operation of the protocol. One such example is a re-staking protocol like EigenLayer, where the ETH used by the Ethereum protocol is reused to secure the economy of other protocols. Consider restaking 10% of your ETH with EigenLayer to perform validation of the new sidechain. Even if all stakers in EigenLayer cooperate to misbehave by attacking the security of the sidechain, the price of ETH is unlikely to drop. Therefore, token toxicity is not transferable to re-staking services, which means that bribery costs are zero.
Penalty doesn't help?
In this section, we explain how slashing can significantly increase the cost of bribes in two scenarios:
Decentralized protocols under bribery;
Token toxicity non-transferable PoS protocol.
prevent bribery

Protocols can use slashing to substantially increase the cost of corruption for external adversaries attempting bribing attacks. To better explain this, we consider the example of a BFT-based PoS chain that requires a stake in the chain's native token and must compromise at least ⅓ of the total stake for any successful attack on its security (in the form of a double-signature form). Assume that an external adversary is able to bribe at least ⅓ of the total stake stake to perform double signing. Proof of double-signing can be submitted to a canonical fork that slashes nodes that accept bribes from their adversaries and double-sign. Assuming that each node stakes S tokens and all confiscated tokens are destroyed, we get the following payoff matrix:
With slashing, if a node agrees to accept a bribe and the attack is unsuccessful, its stake S is slashed in the canonical fork (lower left cell of the matrix), in contrast to the previous bribery scenario where there was no slashing mechanism. On the other hand, even if the attack is successful, the node will not lose its stake S (the upper right cell of the matrix) in the canonical fork. If ⅓ of the total stake needs to be bribed for the attack to succeed, the cost of bribing must be at least 𝑁/3 × S, which is significantly higher than the cost of bribing without slashing.
Protection against toxic non-transferable cases of tokens
In some PoS protocols where token valuation is not affected by protocol security, token toxicity is non-transferable. In many of these systems, the PoS protocol sits on top of another underlying protocol. Then, the base protocol resolves disputes by deploying a dispute resolution mechanism on the base protocol, and grants the base protocol agency rights to confiscate nodes related to the PoS protocol in a provable manner, thereby sharing security with the PoS protocol.
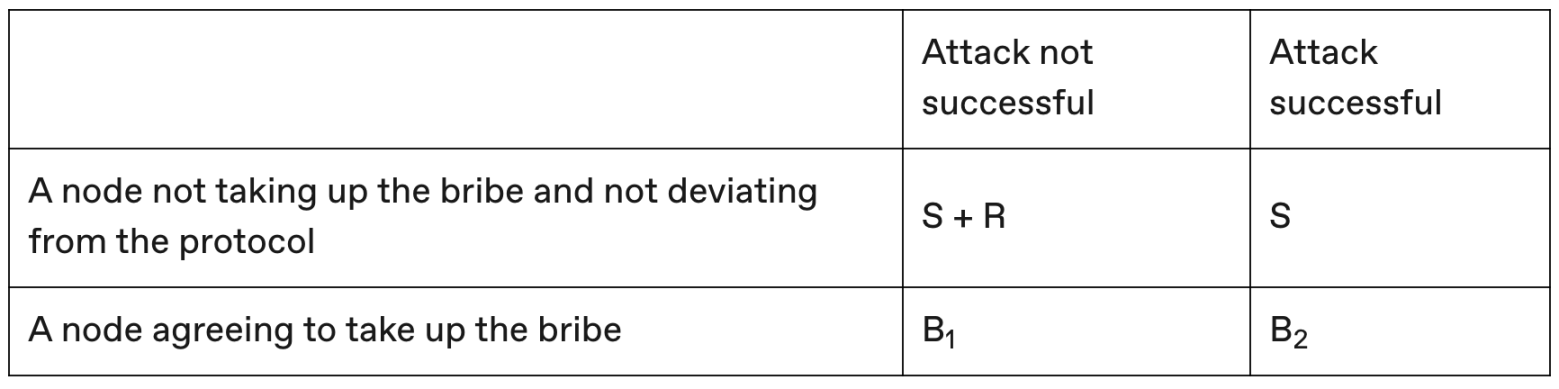
For example, if a Byzantine action in a PoS protocol is objectively attributable to a hostile node in the underlying protocol, its stake in the PoS protocol will be forfeited in the underlying protocol. An example of such a PoS protocol is EigenLayer, which features restaking, enabling different verification tasks to gain security from the Ethereum base protocol. If, in the verification task on EigenLayer, a node adopts a Byzantine strategy for re-staking, where the Byzantine behavior can be objectively attributed, then it can be proved that the node is hostile on Ethereum and its stake will be forfeited how big). Assuming that each node re-stakes S, all confiscated tokens are destroyed, and reward R is obtained from participation, we construct the following reward matrix:
Since we are considering a verification task where any Byzantine behavior can be objectively attributed, even if a node behaves honestly but the attack is successful, the node will not be slashed on Ethereum (top right cell in the matrix). On the other hand, a node that agrees to accept bribes and behaves hostilely will be objectively slashed on Ethereum (bottom row in the matrix). If ⅓ of the total stake needs to be bribed for the attack to succeed, then the cost of bribing is at least 𝑁/3 × S.
We also consider the extreme case where all staked stakes of a PoS protocol are concentrated in the hands of a single node. This is an important scenario because it portends the eventual centralization of stake. Given our assumption that there is no token toxicity for heavily staked tokens, centralized nodes can operate in a Byzantine manner without penalty if there is no slashing. But with slashing, this Byzantine centralized node can be penalized in the base protocol.
Slashing for attributed attacks vs. slashing for non-attributed attacks
There is an important nuance between slashing an attributed attack and slashing a non-attributed attack. Consider the case of a safety failure in a Byzantine Fault Tolerant protocol. Usually, they arise from the Byzantine behavior of double signing and are designed to weaken the security of the blockchain - this is an example of an attribution attack because we can pinpoint which nodes attacked the security of the system. On the other hand, the Byzantine behavior of censoring transactions to impair blockchain liveness is an example of a non-attributable attack. In the former case, slashing is achieved algorithmically by providing evidence of double signatures to the blockchain’s state machine.
In contrast, slashing for censored transactions cannot be done algorithmically, since it cannot be algorithmically proven that nodes are actively censoring. In this case, the protocol may have to rely on social consensus to enforce the slash. A certain percentage of nodes can perform a hard fork to designate slashing of those nodes accused of participating in censorship. Only when social consensus emerges, such a hard fork will be considered a canonical fork.We define the cost of bribery as the minimum cost to perform a security attack. However, we need a property of PoS protocols called accountability, which means that if the protocol loses security, there should be a way to place the blame on a small group of nodes (⅓ nodes for BFT protocols). As it turns out, the analysis of which protocols are responsible is tricky (see the article on BFT protocol forensicspaperPoSAT). Furthermore, it turns out that dynamically available longest-chain protocols (e.g.) are not accountable (for the trade-offs between dynamic availability and accountability, and some approaches to addressing these fundamental trade-offs, see this。)
paper
3. The pitfalls and mitigation measures of confiscation
Like any technology, slashing comes with its own risks if not implemented carefully:
1. The client configuration is wrong/the key is lost. One of the pitfalls of slashing is that innocent nodes may be disproportionately punished for unintentional errors such as misconfigured or lost keys. To address concerns about excessive slashing of honest nodes due to inadvertent mistakes, the protocol could employ certain slashing curves that are less penalized when only a small amount of staked behavior is inconsistent with the Severe penalties will be imposed when the pledged equity executed on the platform exceeds the threshold ratio. For example, Ethereum 2.0 takes this approach.
2. Credible threat of slashing as a lightweight alternative. If a PoS protocol does not implement algorithmic slashing, it can instead rely on the threat of social slashing, i.e., in the event of a security failure, nodes will agree to point to a hard fork where misbehaving nodes lose their funds. This does require significant social coordination compared to algorithmic slashing, but as long as the threat of social slashing is credible, the game-theoretic analysis presented above continues to apply to protocols without algorithmic slashing but instead relying on social slashing of commitments.
3. Social slashing for liveness failures is fragile. Social slashing is necessary to punish non-attributable attacks, such as liveness failures like censorship. While it is theoretically possible to impose social slashing for non-attributable failures, it is difficult for newly joining nodes to verify whether this social slashing is happening for the right reasons (censorship) or because the node was wrongly accused. This ambiguity does not exist when using social slashing for attributable failures, even without a slashed software implementation. Newly joining nodes can continue to verify that this slashing is legitimate because they can check their double signatures, even if only manually.
4. What to do with the confiscated funds?
There are two possible ways to deal with forfeited funds: destruction and insurance.
1. Destruction: The straightforward way to deal with confiscated funds is to simply destroy them. Assuming the total value of tokens has not changed due to the attack, each token will increase in value proportionally and will be more valuable than before. Instead of identifying and compensating only those parties harmed by a security failure, the burn would indiscriminately benefit all non-attacking token holders.
2. Insurance: A more complex forfeiture funding allocation mechanism that has not been studied involves insurance bonds issued against forfeitures. Customers transacting on the blockchain may obtain these insurance bonds in the blockchain in advance to protect themselves from potential security attacks, insuring their digital assets. In the event of a security-compromising attack, algorithmic slashing of stakers generates a fund that can then be distributed to insurers in proportion to the bond.
As far as we know, Vitalik's 2014This articleThis article
The benefits of forfeiting are explored for the first time in . The Cosmos ecosystem built the first efficient implementation of slashing into its BFT consensus protocol, which enforces slashing when validators do not participate in proposing blocks or double-sign ambiguous blocks.
Ethereum 2.0 also includes a slashing mechanism in its PoS protocol, and validators in Ethereum 2.0 may be punished for making ambiguous proofs or proposing ambiguous blocks. Slashing misbehaving validators is the way Ethereum 2.0 achieves economic finality. A validator can also be penalized relatively mildly for missing proofs, or if it doesn't propose blocks when it should.










