

From 2014 to 2026: A Full Review of Global CEX Hacking Incidents
From the first major attack on Mt.Gox in 2011 to the successive thefts at major exchanges such as Binance and Bybit in later years, exchange security issues have never truly disappeared.
Hot wallets, private keys, multi-signature systems, employee computers, and even wallet service providers and third-party security devices have all served as entry points for attackers.
The amounts stolen have continued to rise, and attack methods have grown increasingly sophisticated. Early attackers mainly sought out technical vulnerabilities in the exchanges themselves; later, phishing, malware, and private key theft gradually became common tactics; in recent years, attacks have extended to multi-signature frontends, internal employees, and software supply chains.
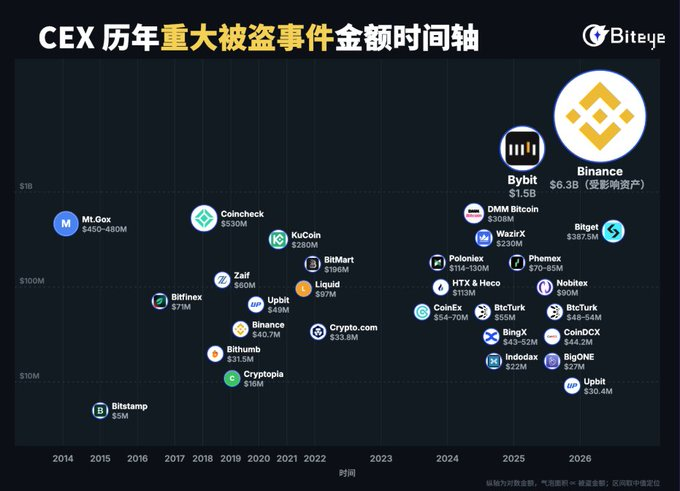
This article compiles publicly disclosed CEX theft incidents throughout history, arranged chronologically, with a focus on the amount stolen and the specific cause of each incident.
TL;DR
- Between 2014 and 2026, there were more than 30 major theft incidents at centralized exchanges, with cumulative losses of approximately $11.3 billion to $11.4 billion calculated at the coin prices at the time of each incident.
- Attack methods have continuously escalated: from early theft of hot wallet private keys to employee phishing, multi-signature interface tampering, and supply chain attacks.
- The amounts stolen have grown larger and the attack paths more covert. Exchanges now need to guard against not only wallets but also employees, permission systems, and third-party services.
- Of these, 15 incidents were attributed or suspected by officials or security agencies to be linked to North Korean hackers, involving approximately $10.1 billion, accounting for nearly 90% of the total amount.
2014
Mt.Gox | $450 million–$480 million
In February 2014, Mt.Gox announced that approximately 850,000 BTC had gone missing, valued at approximately $450 million to $480 million at the time, of which the platform later recovered about 200,000.
Investigations showed that attackers may have gained access to server and wallet private keys as early as 2011 and continuously transferred platform assets. Prolonged theft combined with chaotic internal management ultimately led to Mt.Gox's bankruptcy.
2015
Bitstamp | Approximately $5 million
In January 2015, attackers used social engineering to approach Bitstamp employees, sending files containing malicious programs to system administrators. After the administrator ran the files, the computer was compromised, and files containing hot wallet information were also stolen.
2016
Bitfinex | Approximately $71 million
Bitfinex was cooperating with BitGo to manage multi-signature wallets at the time. After obtaining relevant credentials and API permissions, attackers raised withdrawal limits and bypassed the original multi-signature security mechanism to complete transfers.
2018
Coincheck | Approximately $530 million
Coincheck stored 523 million XEM in a hot wallet without multi-signature protection. After an employee's computer was infected with malware, attackers gained control of the wallet and transferred the assets away.
Bithumb | Approximately $31.5 million
Bithumb's hot wallet was compromised, and approximately 35 billion Korean won worth of assets were transferred out. The specific attack path was not disclosed.
Zaif | Approximately $60 million
Zaif's hot wallet was compromised, and assets including Bitcoin, Bitcoin Cash, and MonaCoin were transferred out.
2019
Cryptopia | Approximately $16 million
Multiple hot wallets at Cryptopia were attacked. After the incident, funds continued to flow out, indicating that attackers likely already possessed the relevant private keys and the exchange could not cut off their control in time.
Binance | Approximately $40.7 million
Attackers used prolonged phishing and malware to collect users' API keys and two-factor authentication information, then launched concentrated withdrawals, transferring 7,000 BTC from Binance's hot wallet.
Upbit | Approximately $49 million
342,000 ETH were transferred out of Upbit's Ethereum hot wallet. Public materials did not disclose the specific process by which attackers obtained wallet permissions.
2020
KuCoin | Approximately $280 million
The private keys of multiple KuCoin hot wallets were leaked, allowing attackers to control the wallets and transfer out Bitcoin, Ethereum, and a large number of ERC-20 tokens.
2021
Liquid | Approximately $97 million
Liquid's warm wallet was compromised, and Bitcoin, Ethereum, and other tokens were transferred out. Although warm wallets are not continuously online, they remain connected to network systems, so the risk of permission compromise still exists.
BitMart | Approximately $196 million
The private keys of BitMart's hot wallets on Ethereum and Binance Smart Chain were stolen. Attackers transferred out tokens in bulk and exchanged assets through decentralized trading platforms.
2022
Crypto.com | Approximately $33.8 million
Attackers bypassed Crypto.com's two-factor verification process and transferred Bitcoin, Ethereum, and other assets from 483 user accounts.
2023
CoinEx | Approximately $54 million–$70 million
CoinEx's hot wallet private keys were leaked. After gaining control, attackers transferred assets in bulk from wallets across multiple chains.
Poloniex | Approximately $114 million–$130 million
Poloniex's hot wallet was attacked, and a large number of tokens were quickly transferred out and exchanged. Attackers most likely had already obtained private keys or equivalent permissions.
HTX and Heco Bridge | Approximately $113 million combined
Abnormal transfers occurred successively in HTX's hot wallet and the Heco Bridge, with both incidents pointing to compromised private keys or high-privilege accounts. Heco is not a centralized exchange, but because of its close relationship with HTX, it is included in the combined tally.
2024
DMM Bitcoin | Approximately $308 million
Attackers approached wallet service provider employees under the guise of recruitment, inducing them to run malicious scripts, then tampered with transfer requests and sent 4,502.9 BTC to attacker addresses.
BtcTurk | Approximately $55 million
Multiple BtcTurk hot wallets were stolen. The specific intrusion method was not disclosed, but attackers had clearly gained control of the hot wallets.
WazirX | Approximately $230 million
The transaction content that WazirX multi-signature personnel saw in the interface did not match what was actually executed on-chain. Attackers exploited this "what you see is not what you sign" discrepancy to induce signers to approve malicious transactions, then upgraded the wallet contract and transferred the assets away.
Indodax | Approximately $22 million
Multiple Indodax hot wallets were attacked. The specific intrusion method was not disclosed; it can only be confirmed that attackers obtained wallet transfer permissions.
BingX | Approximately $43 million–$52 million
Abnormal fund outflows occurred in BingX's hot wallets across multiple chains. Public materials did not disclose the attack entry point; attackers may have controlled private keys or the wallet system.
2025
Phemex | Approximately $70 million–$85 million
Assets were transferred out in bulk from Phemex's hot wallets across multiple chains. The platform did not disclose the initial intrusion path, but attackers had clearly gained control of multiple wallets.
Bybit | Approximately $1.5 billion
Attackers compromised the Safe wallet frontend and tampered with the transaction content seen by multi-signature personnel. Signers believed they were approving normal transfers, but what they actually signed were malicious transactions that modified wallet control, and approximately 400,000 ETH were subsequently transferred out.
Nobitex | Approximately $90 million
Attackers transferred Nobitex's assets to special addresses that no one could control, effectively destroying the funds directly. The main purpose of this attack was not profit but political sabotage.
BigONE | Approximately $27 million
BigONE suffered a supply chain attack. Attackers entered the exchange's server environment and tampered with operating logic, causing the system to transfer assets according to their instructions.
CoinDCX | Approximately $44.2 million
A CoinDCX engineer was tricked by a fake part-time job offer and installed malicious programs on a work computer. Attackers entered the exchange system through the compromised terminal and transferred assets from internal operating accounts.
BtcTurk | Approximately $48 million–$54 million
Abnormal hot wallet transfers occurred at BtcTurk again. The specific intrusion method was not disclosed, but the incident shows that even if most assets are stored in cold wallets, online wallets and permission systems can still become entry points.
Upbit | Approximately $30.4 million
Upbit administrator accounts were stolen. Attackers used high-privilege accounts to initiate unauthorized withdrawals from Solana hot wallets.
2026: Security devices and signing permissions continue to be compromised
Bitget | Approximately $387.5 million
Attackers exploited a zero-day vulnerability in a third-party security device to enter wallet servers, then forged transactions and transferred assets away. The entry point of this attack was not Bitget's own system but an external security product.
Binance | Approximately $6.3 billion in assets affected
A Binance DevOps engineer's computer was compromised. Attackers entered internal service containers and submitted unauthorized withdrawal transactions. The incident involved approximately $6.3 billion in assets; as of now, about $3 billion of that has been frozen, and the final loss is still being tallied.
Final Thoughts: In the AI Era, Pay Even More Attention to Asset Security
CEX thefts are becoming more frequent and the amounts are growing larger.
From 2024 to 2025, there were 12 major incidents, close to the total of the nine years from 2014 to 2022; the amounts stolen and affected from 2025 to 2026 account for more than 70% of the entire tally.
In addition to the growing amount of assets custodied by exchanges, AI is also improving hackers' attack efficiency. It can help attackers quickly gather employee information and generate phishing emails, fake recruitment materials, and malicious programs in bulk.
Therefore, no matter which exchange you use, do not easily click on links in emails or private messages, enable Passkeys, hardware keys, and withdrawal address whitelists where possible, and regularly clean up API permissions you no longer use. Security is no small matter.