

After resuming withdrawals, funds did not decline but instead rose—how did Bitget turn the situation around in just five days?
Author: WhiteRunner
Over the past few years, major security incidents at exchanges have not been uncommon, with attack vectors gradually expanding from hot wallets and signing systems to internal permissions and third-party services. As systems grow increasingly complex, the boundaries exchanges need to defend are also expanding.
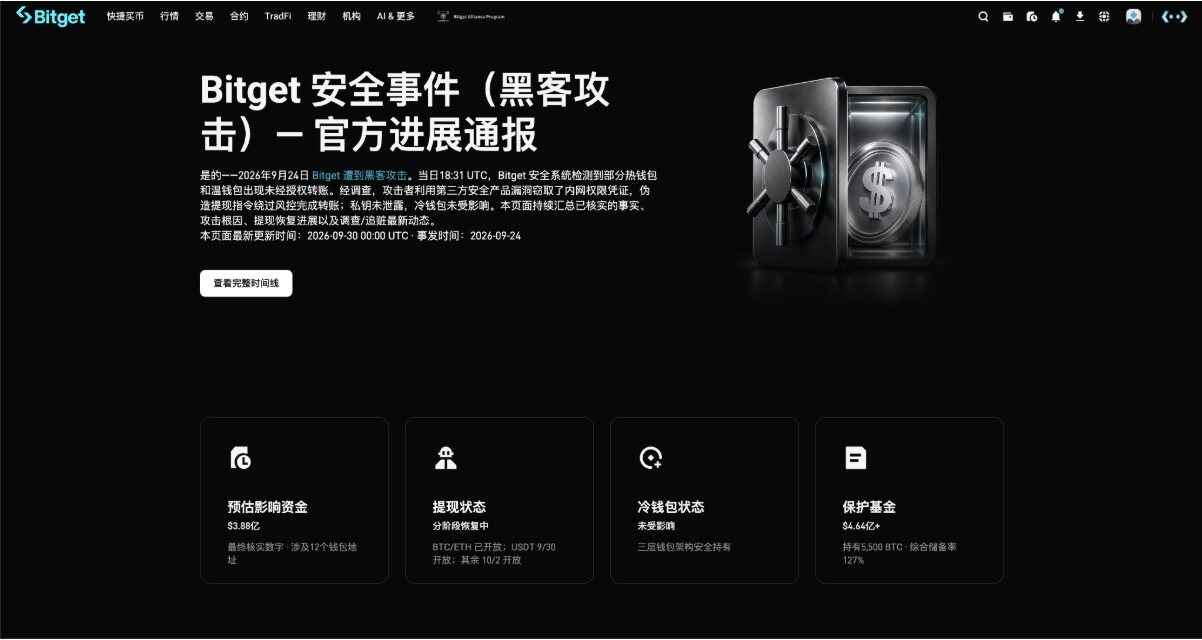
On September 25, Bitget suffered a security incident, ultimately confirming that approximately $388 million in assets were affected. CEO Gracy Chen subsequently stated during a livestream that this was the first such security incident in the platform's eight years of operation. According to investigation results published by SlowMist, the earliest identified malicious activity involved a zero-day vulnerability on a node of a third-party security product. Both Mandiant and SlowMist investigations pointed the attack path to a compromise of third-party security infrastructure, ultimately gaining access to Bitget's wallet environment.
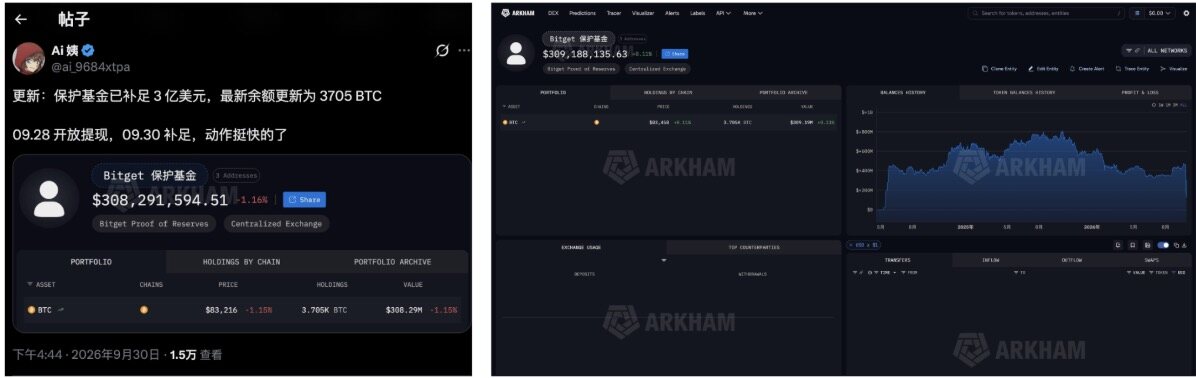
Following the incident, Bitget announced that the User Protection Fund would bear the losses. At the time of the incident, this fund—established in 2022—held 5,500 BTC, valued at over $464 million. Gracy committed that the protection fund would be replenished to $300 million within one week after use, restoring it to the baseline scale established in 2022. On September 30, this commitment was fulfilled as scheduled.
Withdrawals also began resuming according to the previously announced timetable. On September 28 at 16:00, BTC withdrawals were opened first; after ETH withdrawals resumed on September 29, the relevant hot wallets quickly shifted from net outflows to net inflows, and balances soon even slightly exceeded the initial levels before withdrawals were opened—user trust is returning. As of press time, all tokens have resumed withdrawals.
From nearly $400 million stolen to withdrawal resumption and capital flowing back in, only a few days passed. How exactly did the hackers move assets without private keys being leaked? How did a protection fund prepared four years in advance truly come into play? And what did Bitget do to turn the tide of the incident?
1. Hackers Exploited a Zero-Day Vulnerability to Breach a Third-Party Security Product
What makes this attack particularly unusual is that Bitget's private keys were not leaked, the cold wallet was not compromised, and it was not a smart contract vulnerability. The breakthrough the hackers found was actually a third-party security product used by the platform.
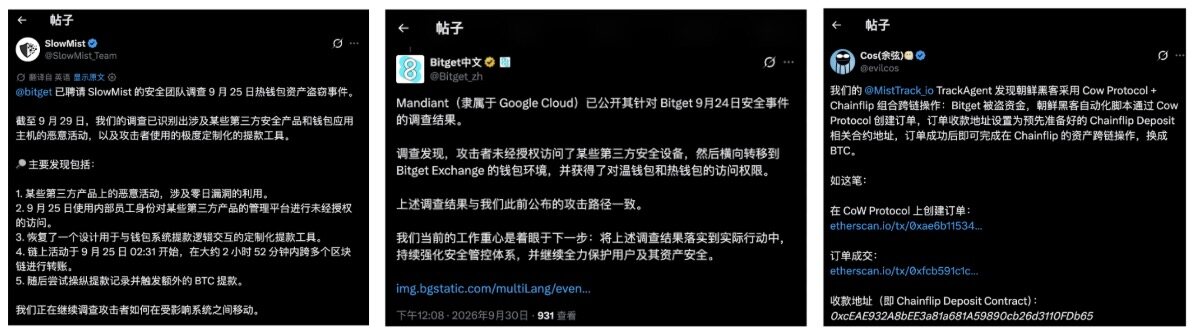
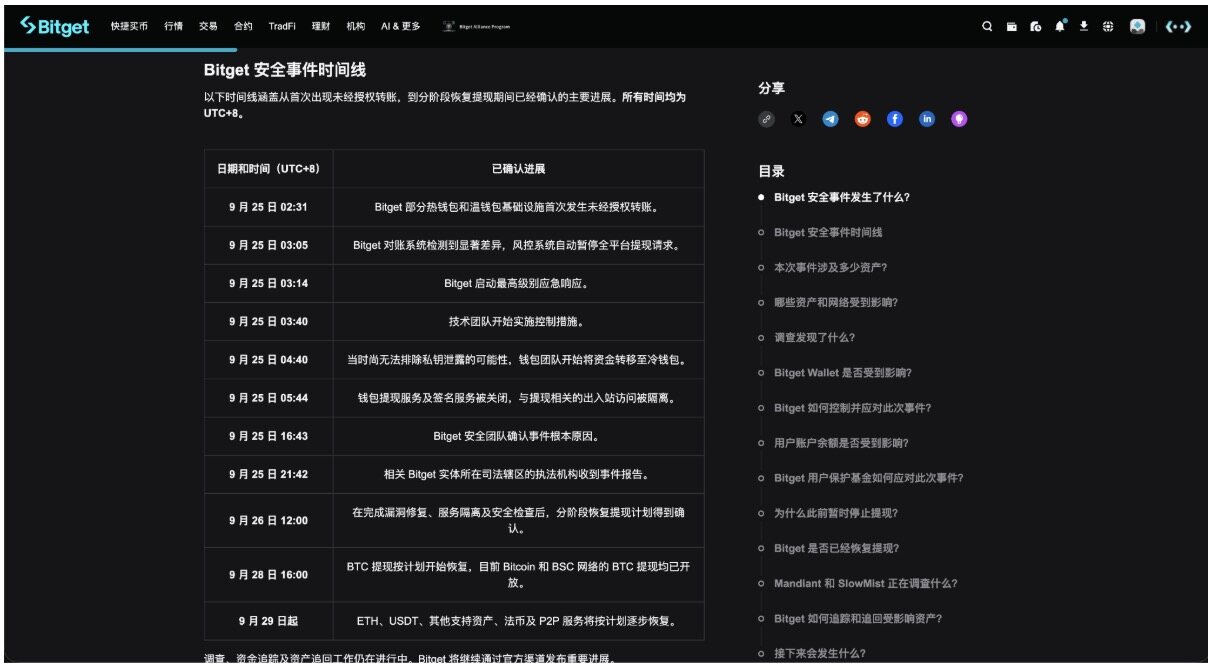
According to investigation results disclosed by Bitget so far, at around 02:31 Beijing time on September 25, the earliest confirmed small transfers appeared on-chain, followed by larger-scale asset transfers.
In an interview with The Block, Gracy stated that from 02:58 to 04:09, the attacker executed 17 large transactions across multiple networks including Ethereum, XRP, Zcash, BNB Chain, Base, Arbitrum, Optimism, and Avalanche. With subsequent statistical updates, Bitget ultimately confirmed that the incident affected approximately $388 million in assets.
At 03:05, approximately 7 minutes after the first large transfer occurred, Bitget's reconciliation system detected significant fund discrepancies and triggered a platform-wide withdrawal block; at 03:14, the platform activated its highest-level emergency response. Since private key compromise could not yet be ruled out at the time, the wallet team subsequently transferred assets to cold wallets and shut down wallet withdrawal and signing services.
Subsequently, the security team confirmed the root cause of the incident. According to the currently disclosed attack chain, the hackers exploited a previously unknown zero-day vulnerability in a third-party security product.
A zero-day vulnerability refers to a security flaw that neither the vendor nor the user was previously aware of and for which no ready-made patch exists to deploy in advance. In other words, this was a previously unknown attack vector. What happened next is the key to understanding this nearly $400 million loss.
Exploiting this vulnerability, the attacker stole internal network credential access through the third-party security product's flaw, forged withdrawal commands to the wallet system, and deceived the wallet into executing abnormal transfers that bypassed risk validation. Throughout the entire process, private keys were not leaked and the cold wallet was not affected.
Gracy later also revealed that the attacker deleted some related traces after completing operations, increasing the difficulty of investigation and reconstructing the attack process.
Bitget subsequently disabled the affected third-party functionality, reissued internal credentials, revoked and re-partitioned highly sensitive permissions, and added independent validation for withdrawals. Mandiant and SlowMist are still participating in independent forensic investigations and fund tracking.
A direct warning this incident leaves for the industry is that the security boundary of exchanges is no longer just private keys and cold wallets. Security software, wallet infrastructure, and other third-party services that can access core systems may themselves become attack vectors.
2. Protection Fund Begins to Be Deployed, Withdrawals Resume on Schedule
After the incident, what truly tests an exchange is who bears the losses when they occur, and how management faces and reassures users.
Bitget first deployed its protection fund.
This fund was established in 2022 and has long maintained a baseline scale of $300 million. At the time of the incident, the fund held 5,500 BTC, valued at over $464 million—sufficient to cover the ultimately confirmed loss of approximately $388 million.
Bitget subsequently made clear that the protection fund would bear the financial impact of this incident, and user account balances would not be affected.
Before BTC withdrawals resumed on September 28, on-chain data already showed the protection fund beginning to allocate assets to hot wallets. On-chain analyst Ai Yi monitored that initially 2,042.28 BTC was transferred from the relevant protection fund address to Bitget's hot wallet (Bitget Protection Fund On-Chain Monitoring).
This is one of the most noteworthy aspects of Bitget's handling of this incident for the industry.
This protection fund was not a compensation plan hastily announced after the incident—it was established four years ago. The funds have been held in long-term reserve, the wallet addresses are publicly verifiable, and there is a clear baseline scale; it was actually deployed after a real incident occurred, and then replenished according to the original standard after use.
The protection fund resolved the issue of who bears the losses. This time, the nearly $400 million loss was ultimately not passed on to users. Gracy stated that Bitget would replenish the protection fund to at least $300 million within one week, and based on on-chain monitoring, this was fulfilled as scheduled.
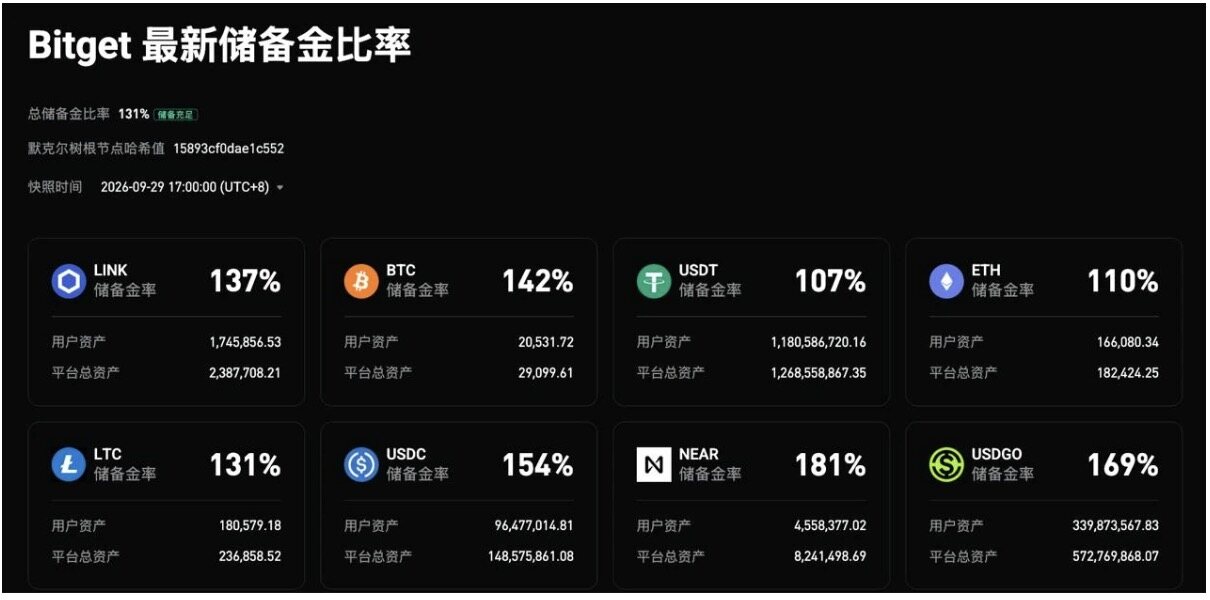
Bitget also published its 47th Proof of Reserves (PoR) on September 30, with a total reserve ratio of 131%, covering 19 types of assets. Among them, the reserve ratios for BTC, ETH, USDT, and USDC were 142%, 110%, 107%, and 154%, respectively.
Beyond the funds, Bitget's communication approach over these past few days also deserves attention.
Gracy responded continuously for approximately three hours during a community-facing livestream, while Xie Jiayin also continuously updated progress through social media and the community. The three-hour livestream itself is not the point—more importantly, during the most chaotic days of the incident, management consistently stood at the forefront answering questions.
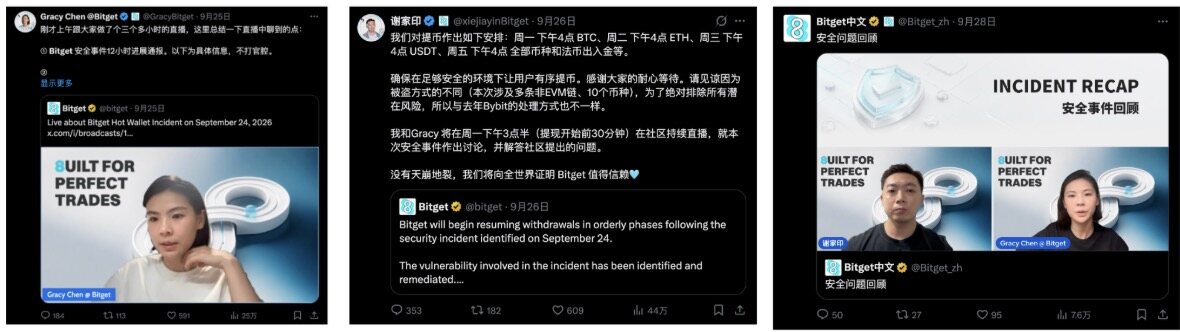
Moreover, several key statements essentially provided clear information or next-step plans.
Who bears the losses was quickly clarified as being covered by the protection fund; after the affected amount was adjusted from $351.6 million to $388 million, the reason for the number change was explained; before the attack vector was confirmed, no rush was made to draw conclusions about the attacker's identity and attack method; after investigation progress was made, details about the third-party security product, zero-day vulnerability, high-privilege credentials, and forged withdrawal commands were gradually disclosed.
The same applies to withdrawal resumption.
This incident involved multiple tokens and multiple networks, and the scope of investigation was not limited to a single wallet. Bitget did not restore all withdrawals at once, but opened them in batches after confirming relevant wallets, networks, and risk elimination one by one.
On September 26, the platform published a specific recovery timetable: BTC on September 28, ETH and related networks on September 29, USDT and related networks on September 30, and other tokens, fiat currencies, and C2C services scheduled for October 2. As of press time, all have been verified as restored on schedule.
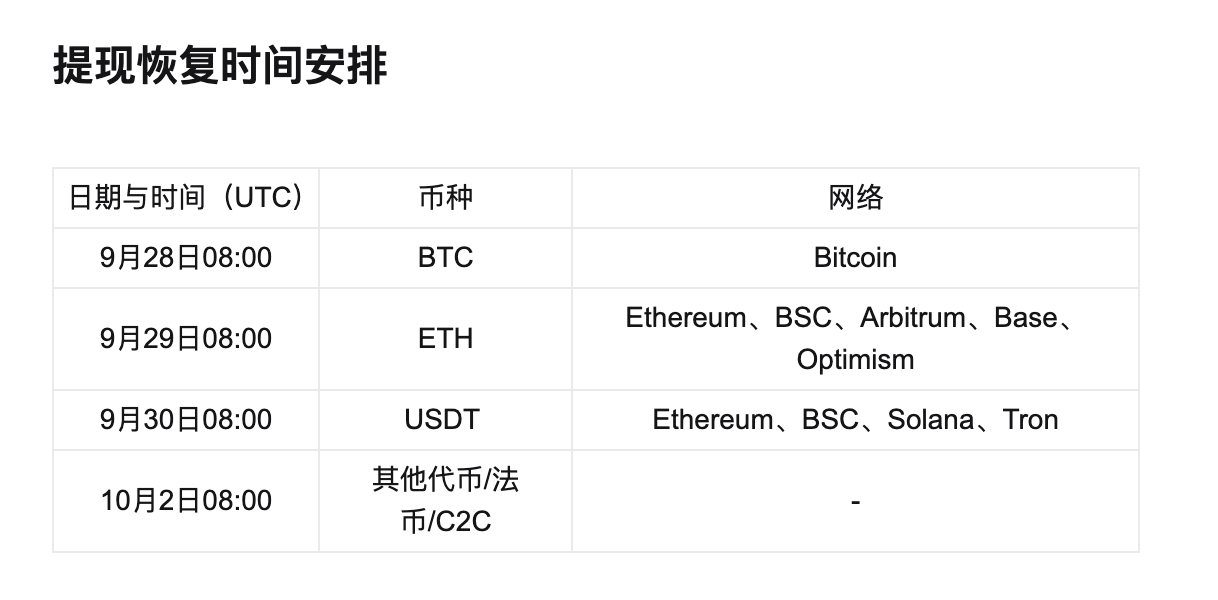
Considering this was a large-scale security incident involving multiple tokens, multiple networks, third-party software, and internal permissions, providing a specific recovery plan down to dates and times, and then delivering on each item one by one, is commendable.
The protection fund was prepared four years in advance and actually used when trouble occurred; management consistently faced the community; confirmed information was disclosed in a timely manner, and unconfirmed information was not rushed to conclusions; the recovery plan gave clear timelines and was executed according to those timelines.
This series of clean and decisive actions led many to view Bitget more positively.
3. The Turning Point Has Emerged, With Capital Flowing Back In
After ETH withdrawals resumed on September 29, a noteworthy change quickly appeared on-chain.
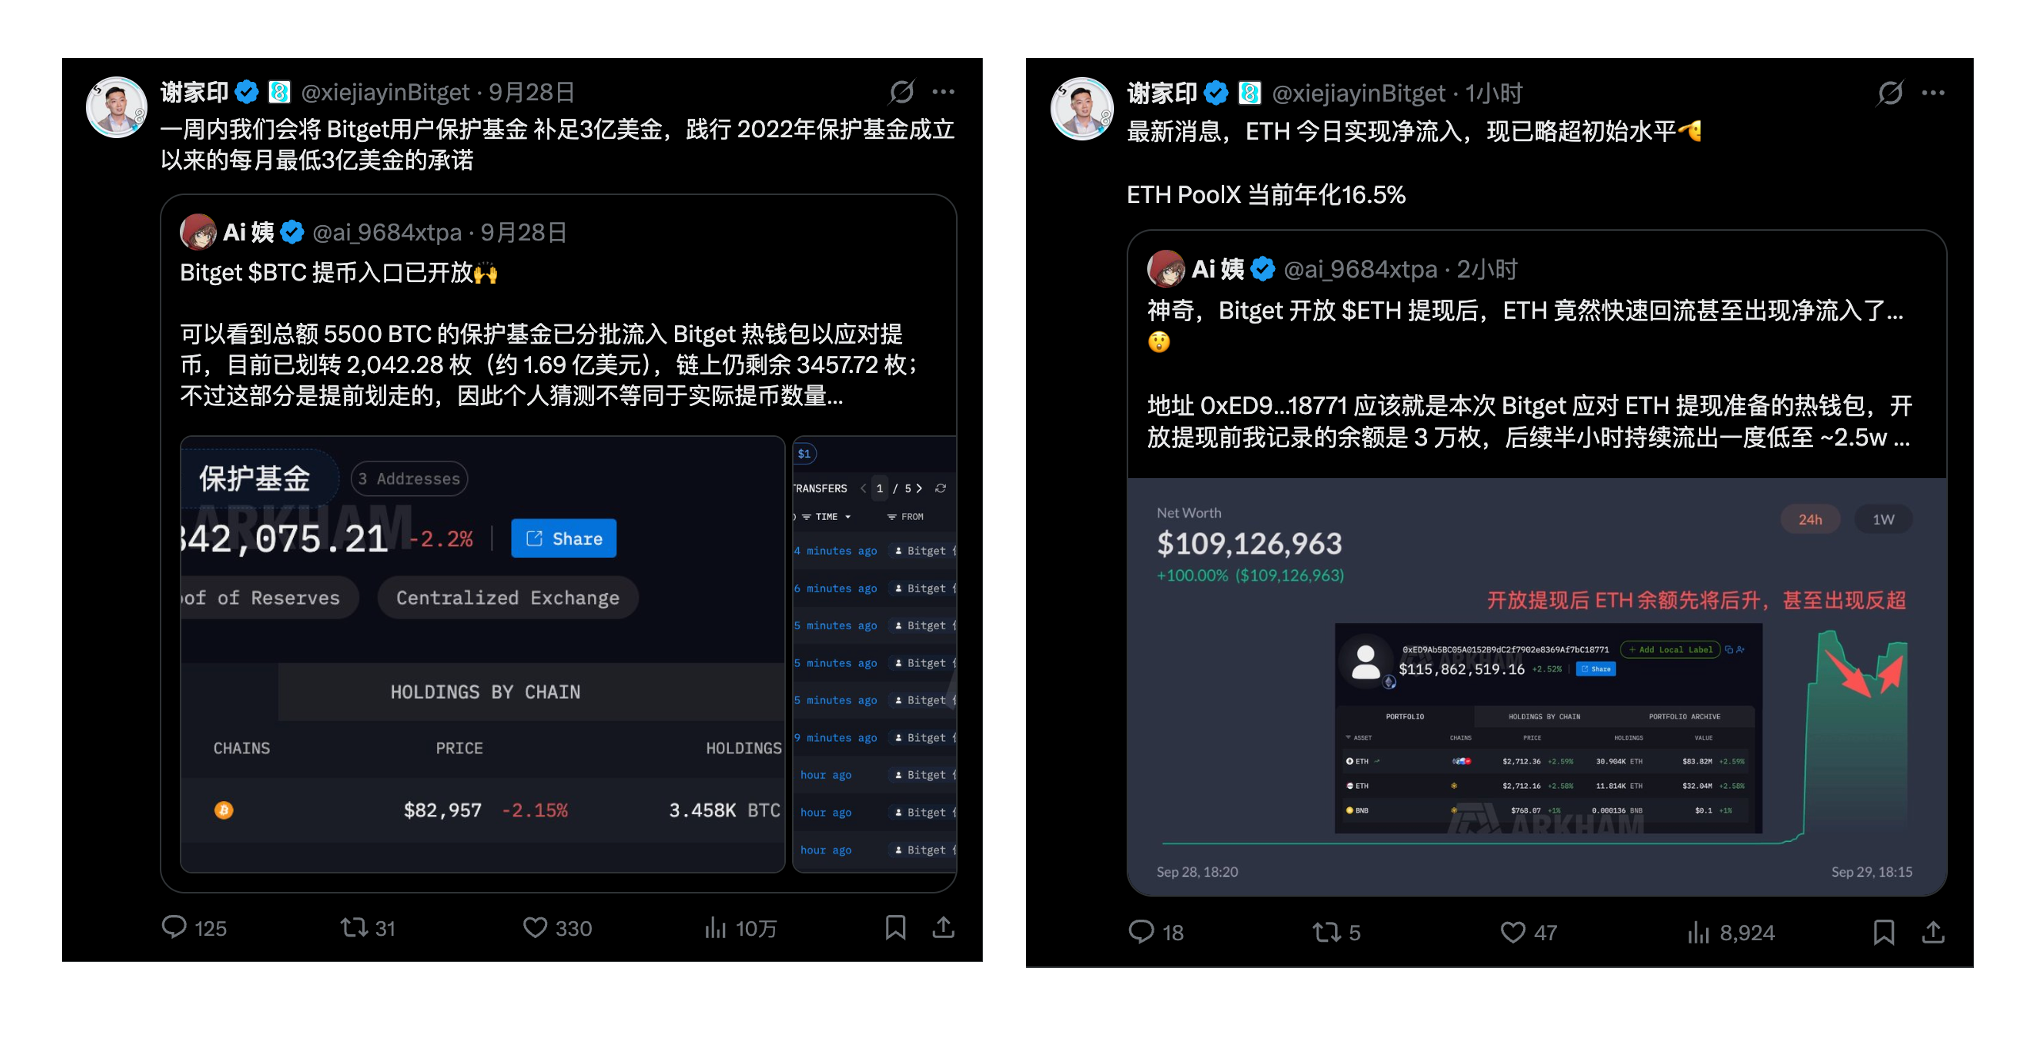
According to monitoring by on-chain analyst Ai Yi, the relevant hot wallet Bitget prepared for ETH withdrawals saw its balance return to over 30,000 ETH—exceeding the initial value—within half an hour after withdrawals opened.
Data subsequently published by Bitget showed that in the first hour after withdrawal resumption, approximately 9,674 ETH flowed in and approximately 9,023 ETH flowed out, for a net inflow of approximately 651 ETH. Data from September 30 showed that 24-hour platform fund inflows reached $231 million, close to the August daily average inflow of $245 million, with no one-directional capital outflow as the market had previously feared—instead, market confidence was visibly recovering.
At the same time, to reward user trust, Bitget also began launching multiple incentive campaigns.
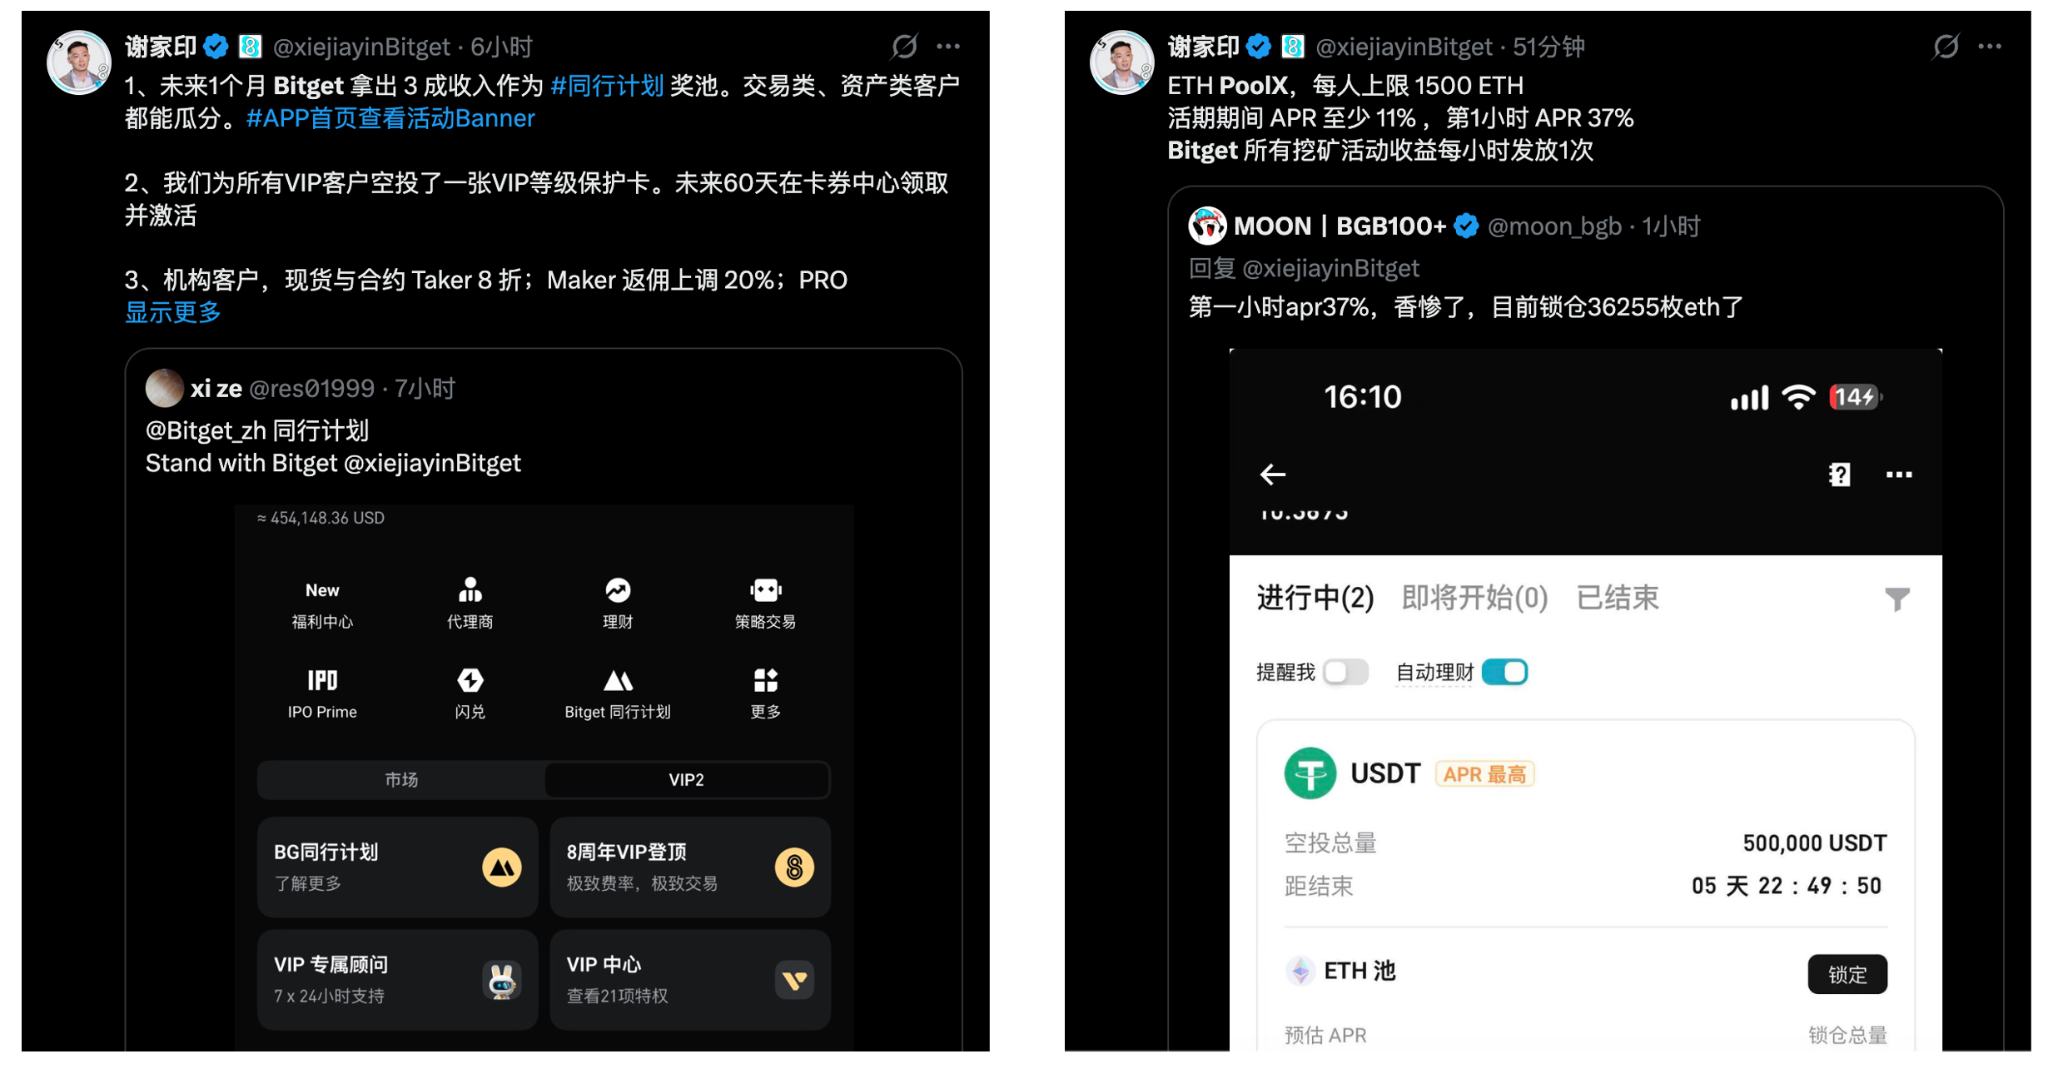
ETH PoolX offered a 500,000 USDT prize pool, allowing users to participate in distribution by locking ETH, with the estimated APR on the campaign page reaching approximately 37.11% in its early phase before dynamically declining as participating funds increased.
BTC PoolX subsequently launched, offering a 100,000 BGB prize pool and providing additional bonuses based on users' prior 15-day BTC holdings.
On the stablecoin side, Bitget simultaneously launched USDT and USDGO flexible savings campaigns, supporting deposit and withdrawal at any time, with limited-time APRs reaching 10% and 12%, respectively. The "Peer Program" allocated 30% of eligible trading fee revenue during the campaign period into a user prize pool, with 60% distributed by trading volume and 40% by asset volume. On October 2, Bitget's official data showed that the first batch of rewards had been distributed, with a cumulative 1,907,455 USDT distributed to 763,543 users.
The intent behind these campaigns is not difficult to understand. Withdrawal resumption addressed the question of whether users "could leave," while the series of campaigns subsequently launched aimed to restart trading, wealth management, and capital retention.
Soon, many users voted with their funds, demonstrating confidence in Bitget and enthusiasm for the campaigns.
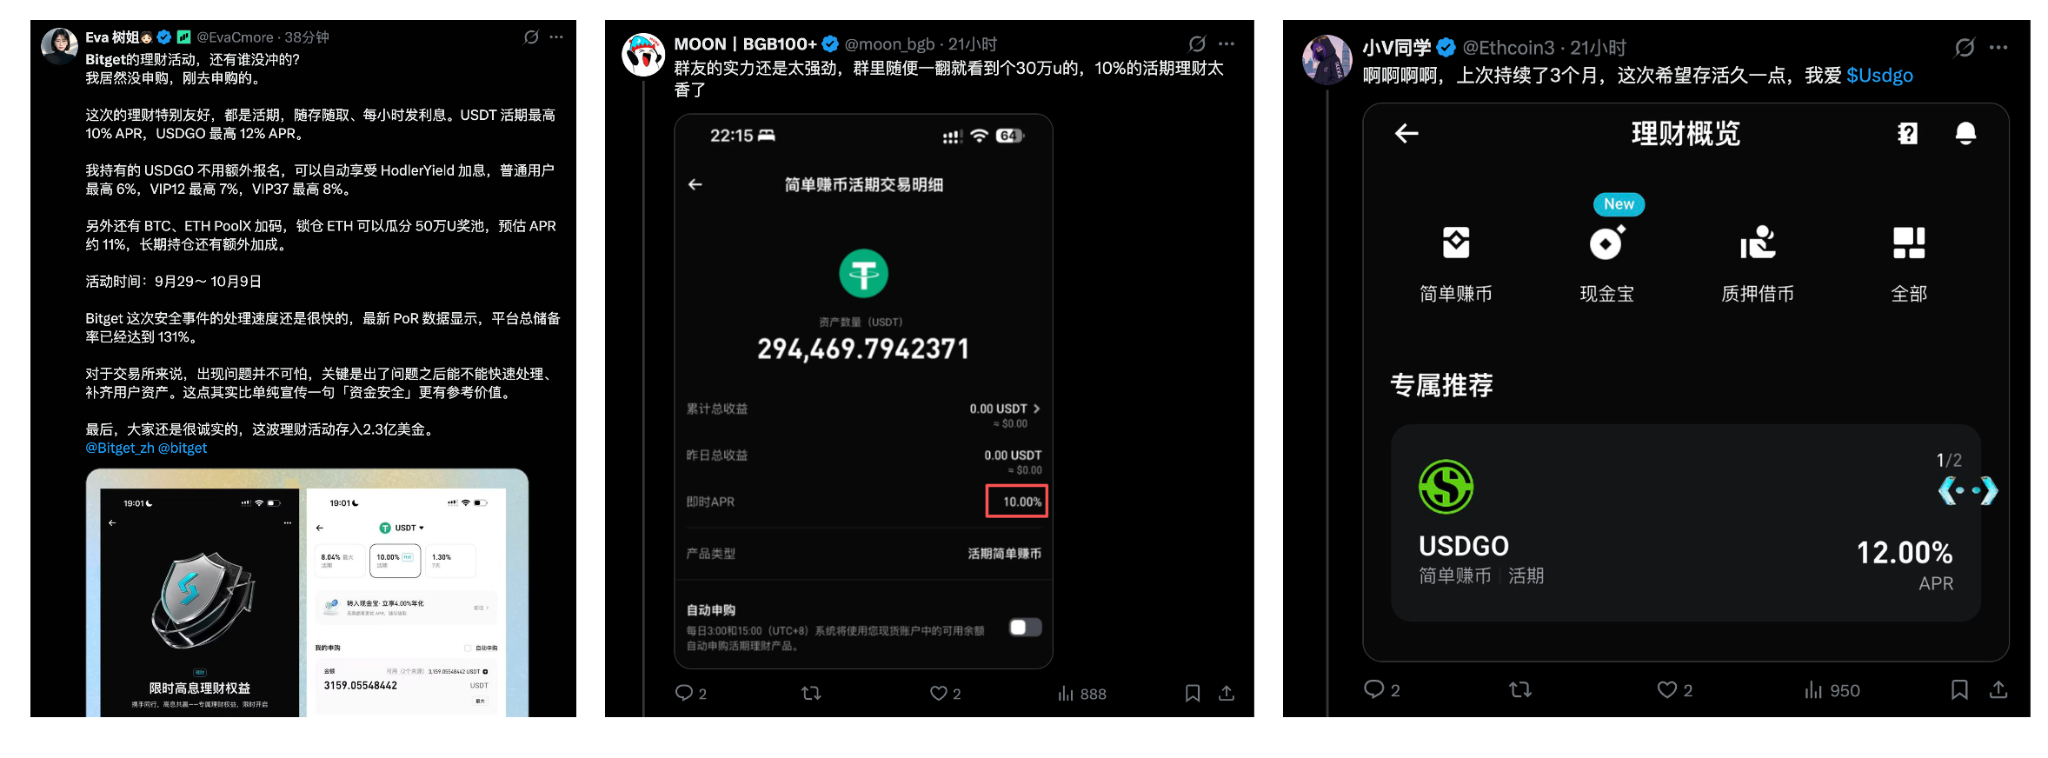
A few days ago, the market's biggest concern was "when can I withdraw my money"; as withdrawals resumed, the question began to shift to "which campaign can earn a higher APR."
A signal that the incident has reached a turning point.
For an exchange, the most direct proof of user confidence recovery is that users are still willing to keep their money there when they are free to come and go.
4. What a Security Incident Has Left for the Exchange Industry
After Bitget's incident, it received support from nearly "half the industry."
The most notable among these is Bybit.
In February 2025, Bybit suffered a security incident of approximately $1.4 billion. About 5 hours after the attack, Bitget provided Bybit with 40,000 ETH, worth over $100 million at the time. These 40,000 ETH came with no interest, no collateral, and no fixed repayment deadline. Bybit subsequently repaid the full amount within three days.
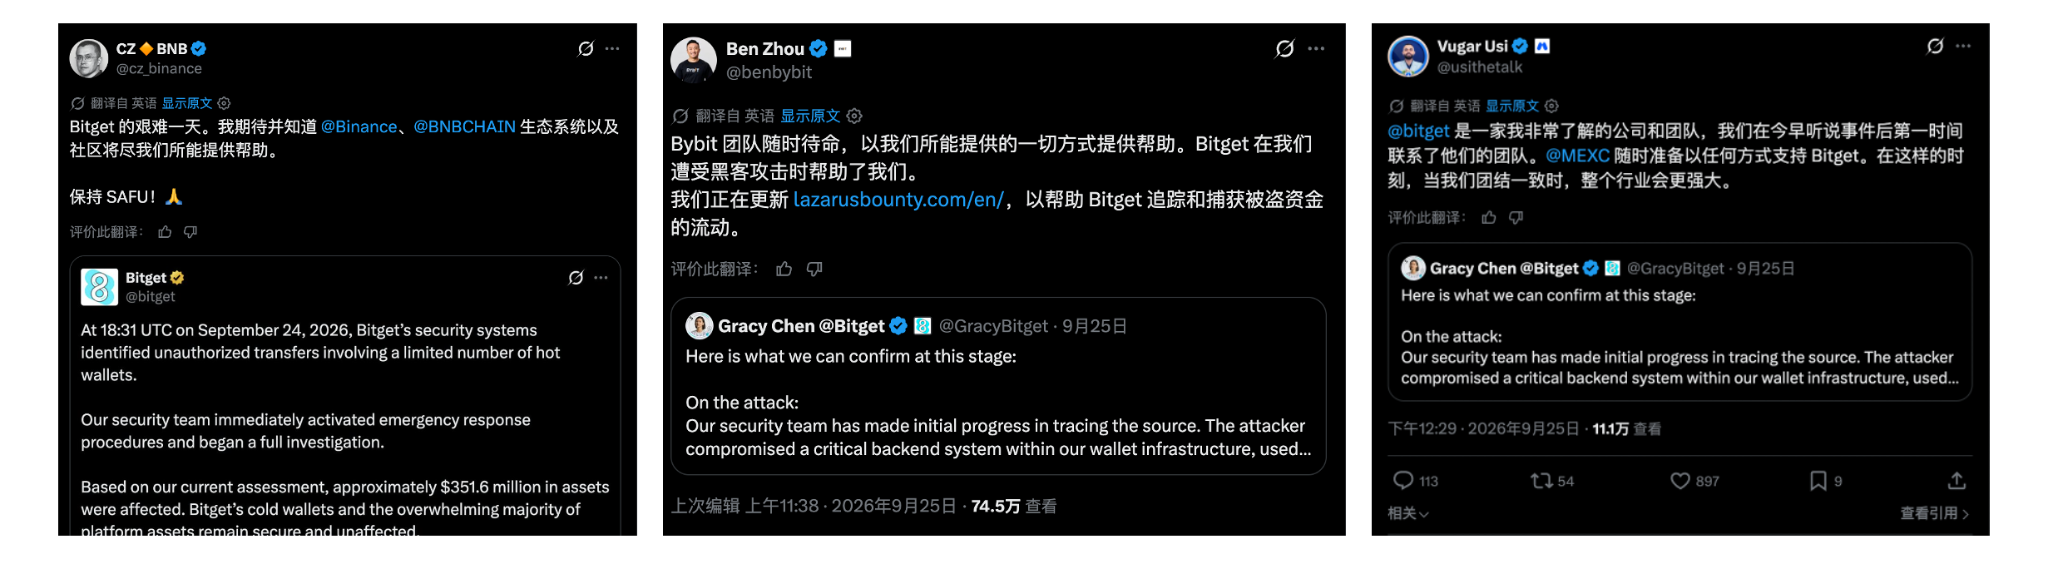
More than a year later, the roles reversed. After Bitget's incident, Bybit CEO Ben Zhou quickly publicly offered help, specifically noting: "When we were hacked, Bitget helped us." Bybit subsequently included the relevant stolen funds in the LazarusBounty tracking system.
It was far from just Bybit that stepped forward. CZ publicly voiced support after the incident, and Binance's security team subsequently collaborated with Bitget, including sharing threat intelligence, tracking stolen funds, and supporting asset recovery; MEXC CEO Vugar Usi also proactively contacted Bitget to express support. Beyond exchanges, Mandiant and SlowMist participated in investigation and forensics, while Circle and Tether participated in freezing relevant assets.
Seeing this news, I did feel a surge of excitement.
The crypto industry has never lacked competition. Exchanges compete for users, liquidity, and market share, but when a security crisis involving hundreds of millions of dollars truly arises, peers still band together for mutual support.
And whether Bitget as a platform has truly earned trust and respect in the industry is most intuitively demonstrated in times of crisis.
But if this matter only remains at the level of "a friend in need is a friend indeed," its significance would be underestimated.
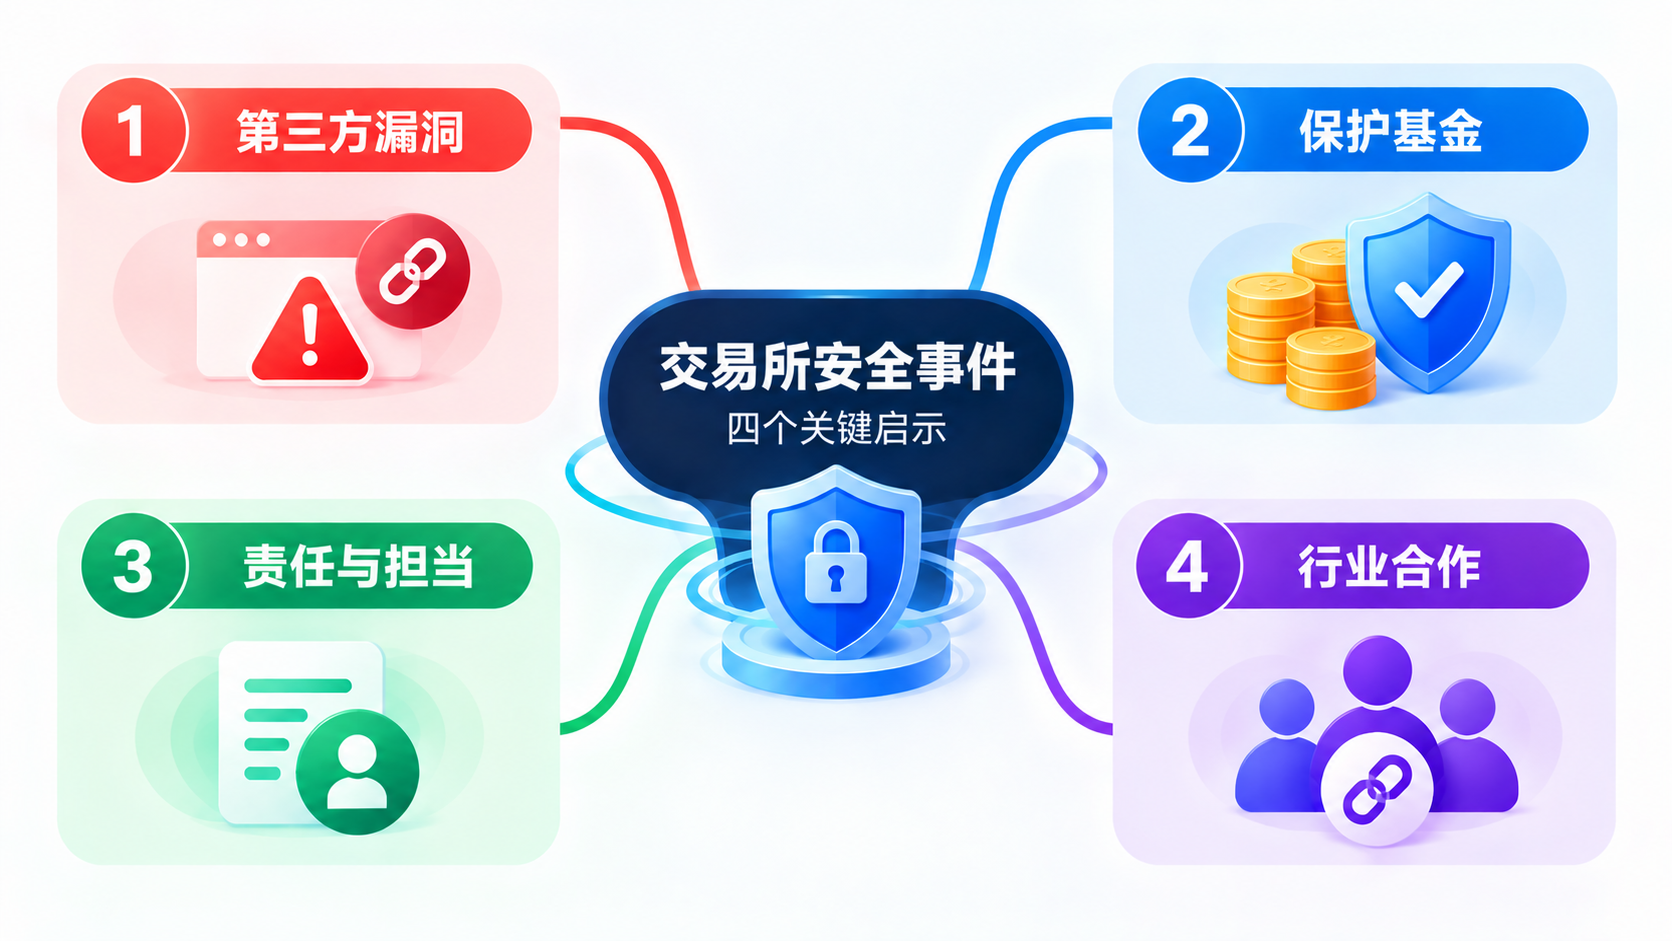
The crypto industry has no unified institution to provide a backstop, but protection funds, peer collaboration, security firms, and on-chain tracking are forming their own risk management network. At the same time, from hot wallets and signing systems to third-party software and internal permissions, the boundaries exchanges need to defend are expanding: attacks are becoming increasingly complex, and the industry needs to respond together.
Establishing protection funds, maintaining openness and transparency afterward while honoring commitments, and industry collaboration are now excellent paradigms for crisis response—and Bitget has now earnestly demonstrated this.
Over the past two years, the crypto industry has been talking about Mass Adoption. ETFs, stablecoins, RWA, and tokenized securities are bringing more traditional financial capital in, and the U.S. regulatory framework is gradually being established. Having reached this point, what the industry needs to prove is no longer just innovation and growth, but also the ability to handle risk.
Bitget this time used $400 million to test a platform's sense of responsibility in the face of crisis. A crisis will not end a platform, but accountability can redefine one.
For the crypto industry that is moving toward mainstream finance, this is also an exam it must undergo. No financial system can be built on the assumption of "never having problems." When problems truly occur, whether you can afford to pay, explain clearly, and recover—that is what tests responsibility and bottom lines.
How the financial world ultimately views the crypto industry may depend on how it properly handles a bad day.