





CertiK: SushiSwap Smart Contract Vulnerability Event Analysis
secondary title
Image Source:
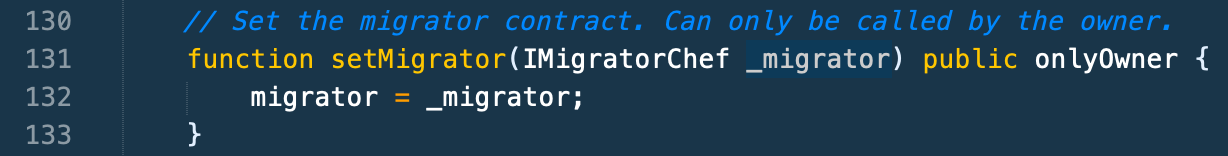
MasterChief.sol:131
Image Source:https://github.com/sushiswap/
Image Source:
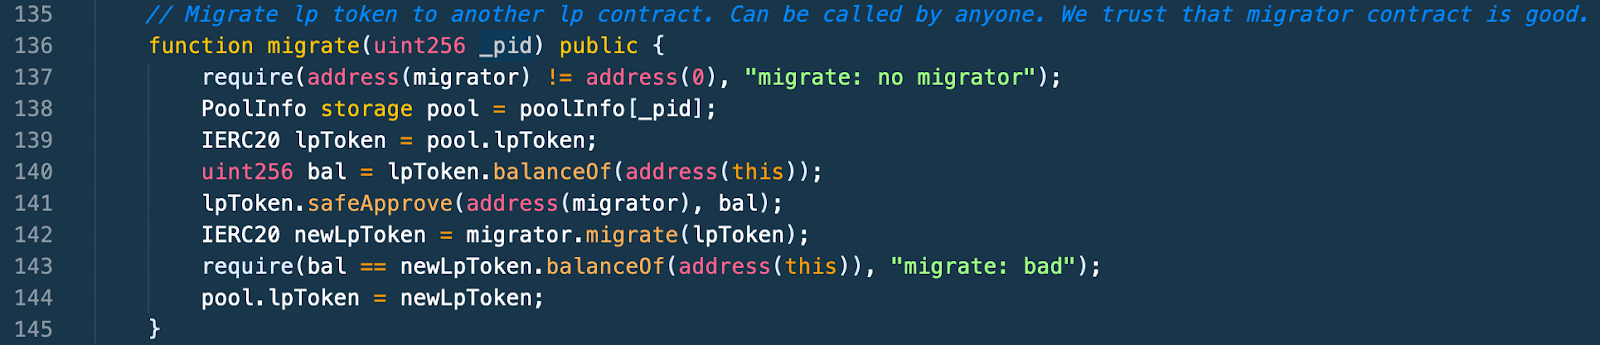
MasterChief.sol:136 。
Image Source:https://github.com/sushiswap/
After the value of migrator is determined (as shown in line 142 in the figure above), migrator.migrate(lpToken) can also be determined accordingly. The method of migrate is called through the interface of IMigratorChef, so when calling, the logic code in the method of migrate will change according to the value of migrator.
In short, if the smart contract owner points the value of migrator to a smart contract containing malicious migrate method code, then the owner can perform any malicious operations he wants, and may even take out all the tokens in the account.
secondary title
Enlightenment of this vulnerability (emphasis added)
· Smart contract owners should not have unlimited rights. Community supervision and governance (governance) must be used to limit smart contract owners and ensure that they will not use their own advantages to conduct malicious operations.
· The smart contract code needs to undergo strict security verification and inspection before it can be released.
The creator of the current SushiSwap project stated that the project has been migrated to a time-locked (Timelock) contract, that is, any SushiSwap project smart contract
Some operations will have a 48-hour delay lock.
Here, the CertiK technical team recommends that you try to find a professional team to do the audit work before the smart contract is announced, so as to avoid loopholes in the project and cause losses.










