





3億美元DeFi資金大遷徙:LayerZero跌倒,Chainlink吃飽
Original author: Nancy, PANews
As several leading protocols have stepped in to provide funding, quickly closing the capital gap and advancing on-chain repairs, the rescue efforts following the Kelp DAO attack have recently seen substantial progress. However, compared to financial recovery, restoring market trust remains the more difficult challenge.
LayerZero, the cross-chain leader at the center of this storm, is facing an accelerated exodus of protocols and has been forced into a drastic shift in attitude within just a few weeks – from initially shifting blame to now publicly apologizing and initiating corrective measures. Meanwhile, Chainlink has unexpectedly emerged as a beneficiary of this crisis, with its CCIP protocol absorbing a significant amount of migrated liquidity and seeing a notable increase in on-chain data.
$3 Billion Migrated in a Single Week: Chainlink Capitalizes on Security Concerns
As the largest DeFi security incident to date in 2026, the Kelp DAO attack has accelerated the migration of on-chain liquidity.
As the security controversy surrounding LayerZero continues to escalate, an increasing number of DeFi protocols are reassessing their cross-chain risks and actively seeking more reliable havens. Over the past week, Chainlink has announced multiple migration cases.
On May 9th, Chainlink officially disclosed that four protocols, including Kelp DAO, Solv Protocol, Re, and Tydro, had recently abandoned their original cross-chain bridge or oracle solutions in favor of migrating to Chainlink CCIP. The combined TVL of these related protocols exceeds $30 billion. Chainlink even coined the term "The Great Migration" to promote this ecosystem shift, adding a distinctly competitive tone.
Behind this wave of migrations is a realignment based on security concerns.
Besides DeFi protocols switching sides due to security worries, Chainlink has also been continuously gaining favor from traditional financial institutions and crypto projects in recent months.
In March this year, Coinbase used Chainlink's newly launched DataLink service to put its exchange market data directly on-chain for the first time. Amundi, Europe's largest asset manager, partnered with Spiko to launch a tokenized public fund based on Chainlink.
In April, OpenAssets entered a strategic partnership with Chainlink to launch an asset tokenization infrastructure solution for institutions. SIX Group, the operator of major European stock exchanges, collaborated with Chainlink to bring Swiss and Spanish stock market data on-chain. AWS Marketplace listed Chainlink's data services, connecting traditional cloud services with blockchain.
In May, the Depository Trust & Clearing Corporation (DTCC) announced it would introduce Chainlink to build a blockchain-based collateral management platform, aiming for near-real-time, 24/7 settlement. Huma Finance partnered with Chainlink to introduce institutional-grade yield products into a multi-chain ecosystem.
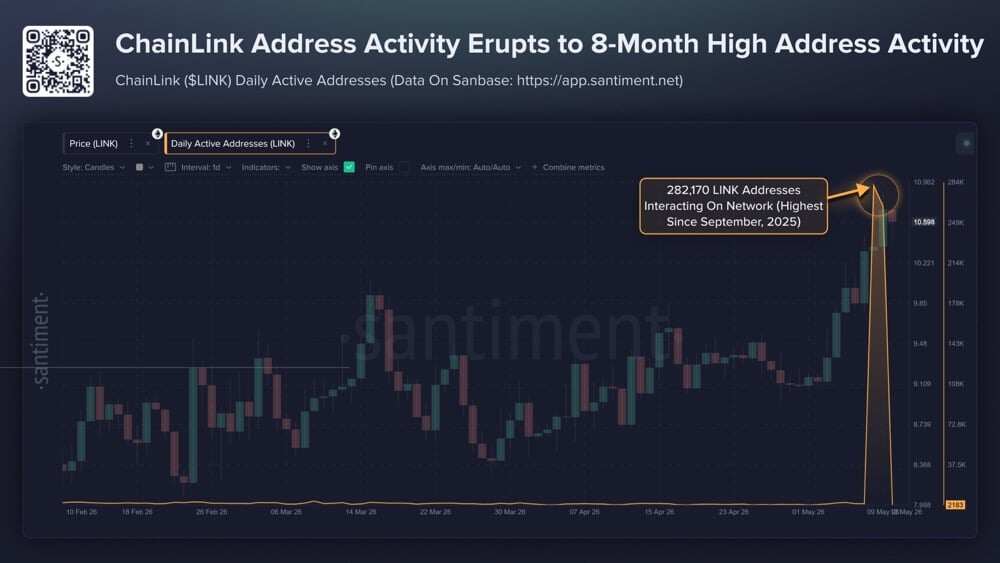
Alongside this continuous ecosystem expansion, Chainlink's on-chain activity has also notably heated up. According to Santiment monitoring, Chainlink's unique active addresses on May 9th and 10th exceeded 282,000 and 264,000 respectively, setting a new high since September 2025. Santiment attributed this primarily to the recent large-scale migration of DeFi protocol infrastructure.
Meanwhile, Chainlink official data shows that the total value of its cross-chain tokens has exceeded $61.8 billion, with CCIP transaction volume reaching $19.5 billion.
Market confidence is also reflected in the changes in LINK token holdings. According to Santiment monitoring earlier this month, over the past month, Chainlink whale and shark addresses holding between 100,000 and 10 million LINK accumulated an additional 32.93 million LINK. Historically, this is often a strong bullish signal. Over the past 30 days, LINK has risen by approximately 19.7%.
LayerZero Faces Trust Crisis, Issues Emergency Apology and Rectification
Currently, LayerZero is mired in a crisis of trust.
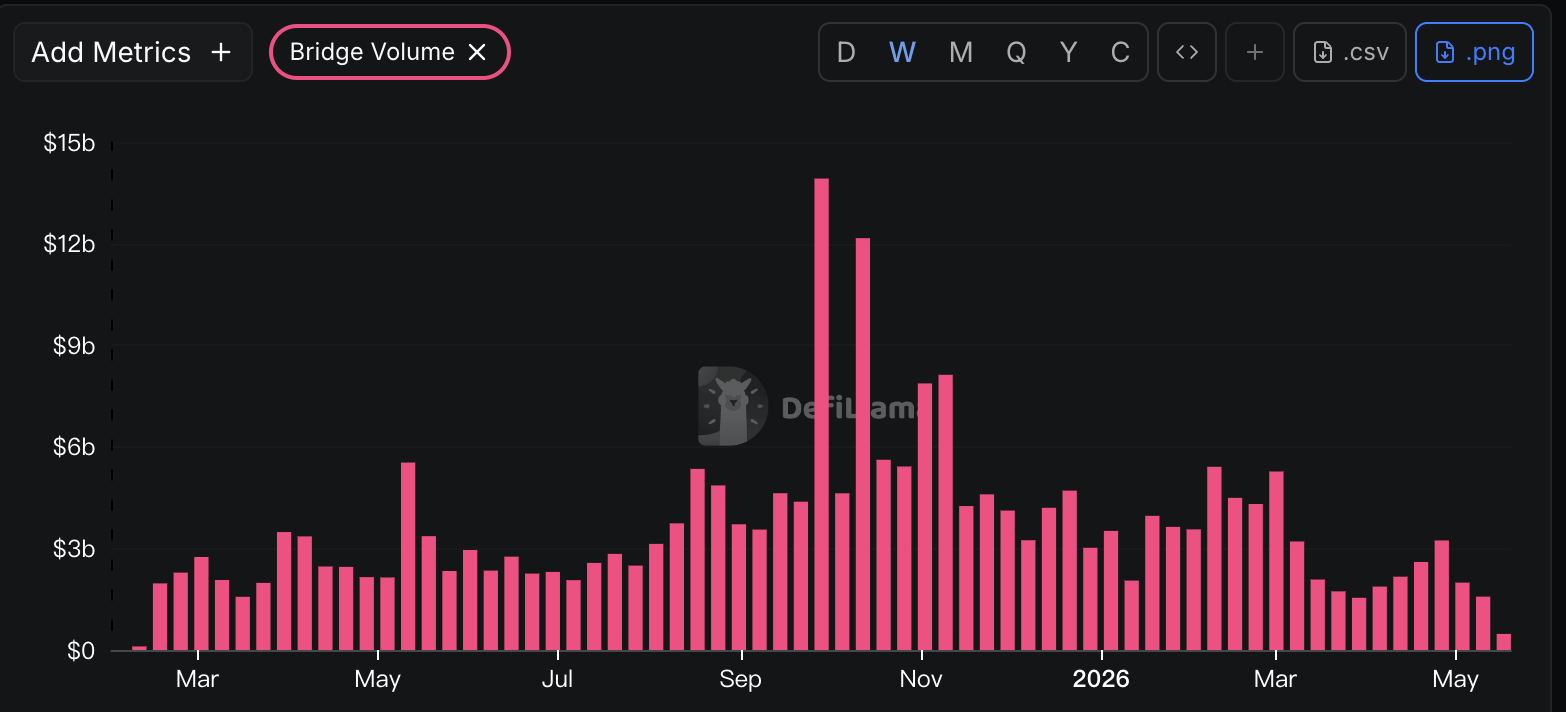
Data from DefiLlama shows that LayerZero's current weekly Bridge transaction volume has dropped to approximately $470 million, approaching historic lows. This attack incident has plunged LayerZero into a trust crisis.
In the early stages of the hack, Kelp DAO attributed the vulnerability attack to LayerZero's security issues. Subsequently, LayerZero quickly denied responsibility, stating that Kelp DAO's multiple allegations regarding the rsETH security incident were entirely false.
However, the controversy did not subside. Last week, LayerZero Labs co-founder and CEO Bryan Pellegrino engaged in a heated argument with several security researchers in the ETHSecurity Community Telegram group.
The core of the controversy was that LayerZero Labs could immediately upgrade default library contracts without a timelock, theoretically allowing the forgery of cross-chain messages. This exposed over $30 billion in LZ OFT assets to potential risk over the past period. Security researcher Banteg pointed out that some major projects, including Ethena and EtherFi, were still using this default library just weeks ago, and approximately $178 million in assets remain exposed to risk.
Simultaneously, on-chain data also revealed that LayerZero multi-signature wallet addresses had engaged in Meme coin trading, DEX swaps, and cross-chain bridging – activities unrelated to their signing duties – further raising community concerns about key security. In response, Bryan acknowledged that these operations were indeed carried out by multi-signature team members but denied they were "Meme coin speculative trades," claiming the purpose was merely "testing PEPE OFT functionality," and stated that the relevant member had been removed.
To mitigate risk, Bryan also publicly recommended that projects adopt "fixed configurations" instead of the default ones as soon as possible. Subsequently, Banteg published a list of LayerZero projects still using the default library contract and urged the relevant protocols to migrate promptly.
These remarks quickly sparked industry discussion and criticism. Chainlink's Head of Strategy, Zach Rynes, publicly criticized LayerZero Labs, stating that its multi-signature keys had suffered from severe OPSEC (Operations Security) failures for a long time, directly exposing billions of dollars in OFT assets to security risks. He further stated that if LayerZero and the industry had truly heeded the continuous warnings from security researchers over the past few years, such an attack could have been entirely avoided.
Faced with market backlash and an ongoing exodus from its ecosystem, LayerZero's attitude has shown a clear shift. On May 9th, LayerZero officially issued a public apology statement, responding to the security incident and communication issues of the past three weeks.
LayerZero Labs stated that its internal RPC had been attacked by the Lazarus Group over the past three weeks, compromising the true source of its DVN (Decentralized Verification Network), while its external RPC provider suffered a DDoS attack. This incident affected only 0.14% of applications and approximately 0.36% of asset value. The LayerZero protocol itself was not affected, and over $90 billion in assets continued to flow normally across chains after the event.
However, LayerZero Labs also admitted for the first time that it had previously allowed DVNs to provide security for high-value transactions with a "1/1" single-node configuration, creating a single point of failure risk, for which it accepted management oversight responsibility. The official statement also disclosed that, three and a half years prior, a multi-signature signer had misused a multi-signature hardware wallet for personal transactions. That signer has been removed, and the relevant wallet has been rotated.
Regarding subsequent rectifications, LayerZero Labs announced a series of security upgrade measures, including ceasing support for 1/1 DVN configurations, migrating all path default configurations to 5/5 multi-signature (minimum 3/3), developing a second DVN client based on Rust for client diversity, launching a dedicated multi-signature tool called OneSig to enhance signing security, and launching a unified management platform, Console, for asset issuance configuration and anomaly detection.
Additionally, LayerZero contributed over 10,000 ETH to the DeFi United rescue operation, with 5,000 ETH allocated to a fund and the remaining 5,000 ETH reserved for Aave.
Despite the escalating controversy, LayerZero has not completely lost the market. Major assets including Ethena's USDe product, EtherFi's weETH asset, and BitGo's WBTC continue to use LayerZero's OFT standard.
Every major security crisis represents a redistribution of liquidity and influence. As the crypto industry gradually moves towards mainstream financial markets, the criteria for evaluating underlying infrastructure will become increasingly stringent, and security capabilities are emerging as a core competitive advantage.










