

Renowned white-hat hacker's undercover exposé of a Chinese money laundering syndicate
Source: ZachXBT
Compiled by Odaily (@OdailyChina); Translator: Azuma (@azuma_eth)
Editor's Note: This is a new article by renowned white-hat hacker ZachXBT about his prior undercover investigation into a Chinese money laundering group. In the article, ZachXBT describes how he posed as a client in need of money laundering services and details his communications with members of the group. After gaining the trust of a group member, ZachXBT learned from them that the group had personally laundered the vast majority of the nearly $1.5 billion stolen from Bybit. After obtaining certain leads through his investigation, ZachXBT also helped freeze some of the stolen funds and passed the leads on to law enforcement.
The following is the original content from ZachXBT, compiled by Odaily.
I recently went undercover to infiltrate an organized Chinese criminal group that had laundered over $1 billion for the North Korean hacking group Lazarus Group across multiple hacking incidents.
Posing as a client, I gathered intelligence, helped freeze funds stolen in the February 2025 Bybit hack, and completed on-chain tracing and attribution of the illicit activity.
It started in February 2025, shortly after the North Korean hacking group "TraderTraitor" stole $1.5 billion from Bybit, when I noticed an anomaly — more than 15 accounts were publicly posting in Telegram and Discord public groups seeking customer support for orders directly linked to the stolen funds.
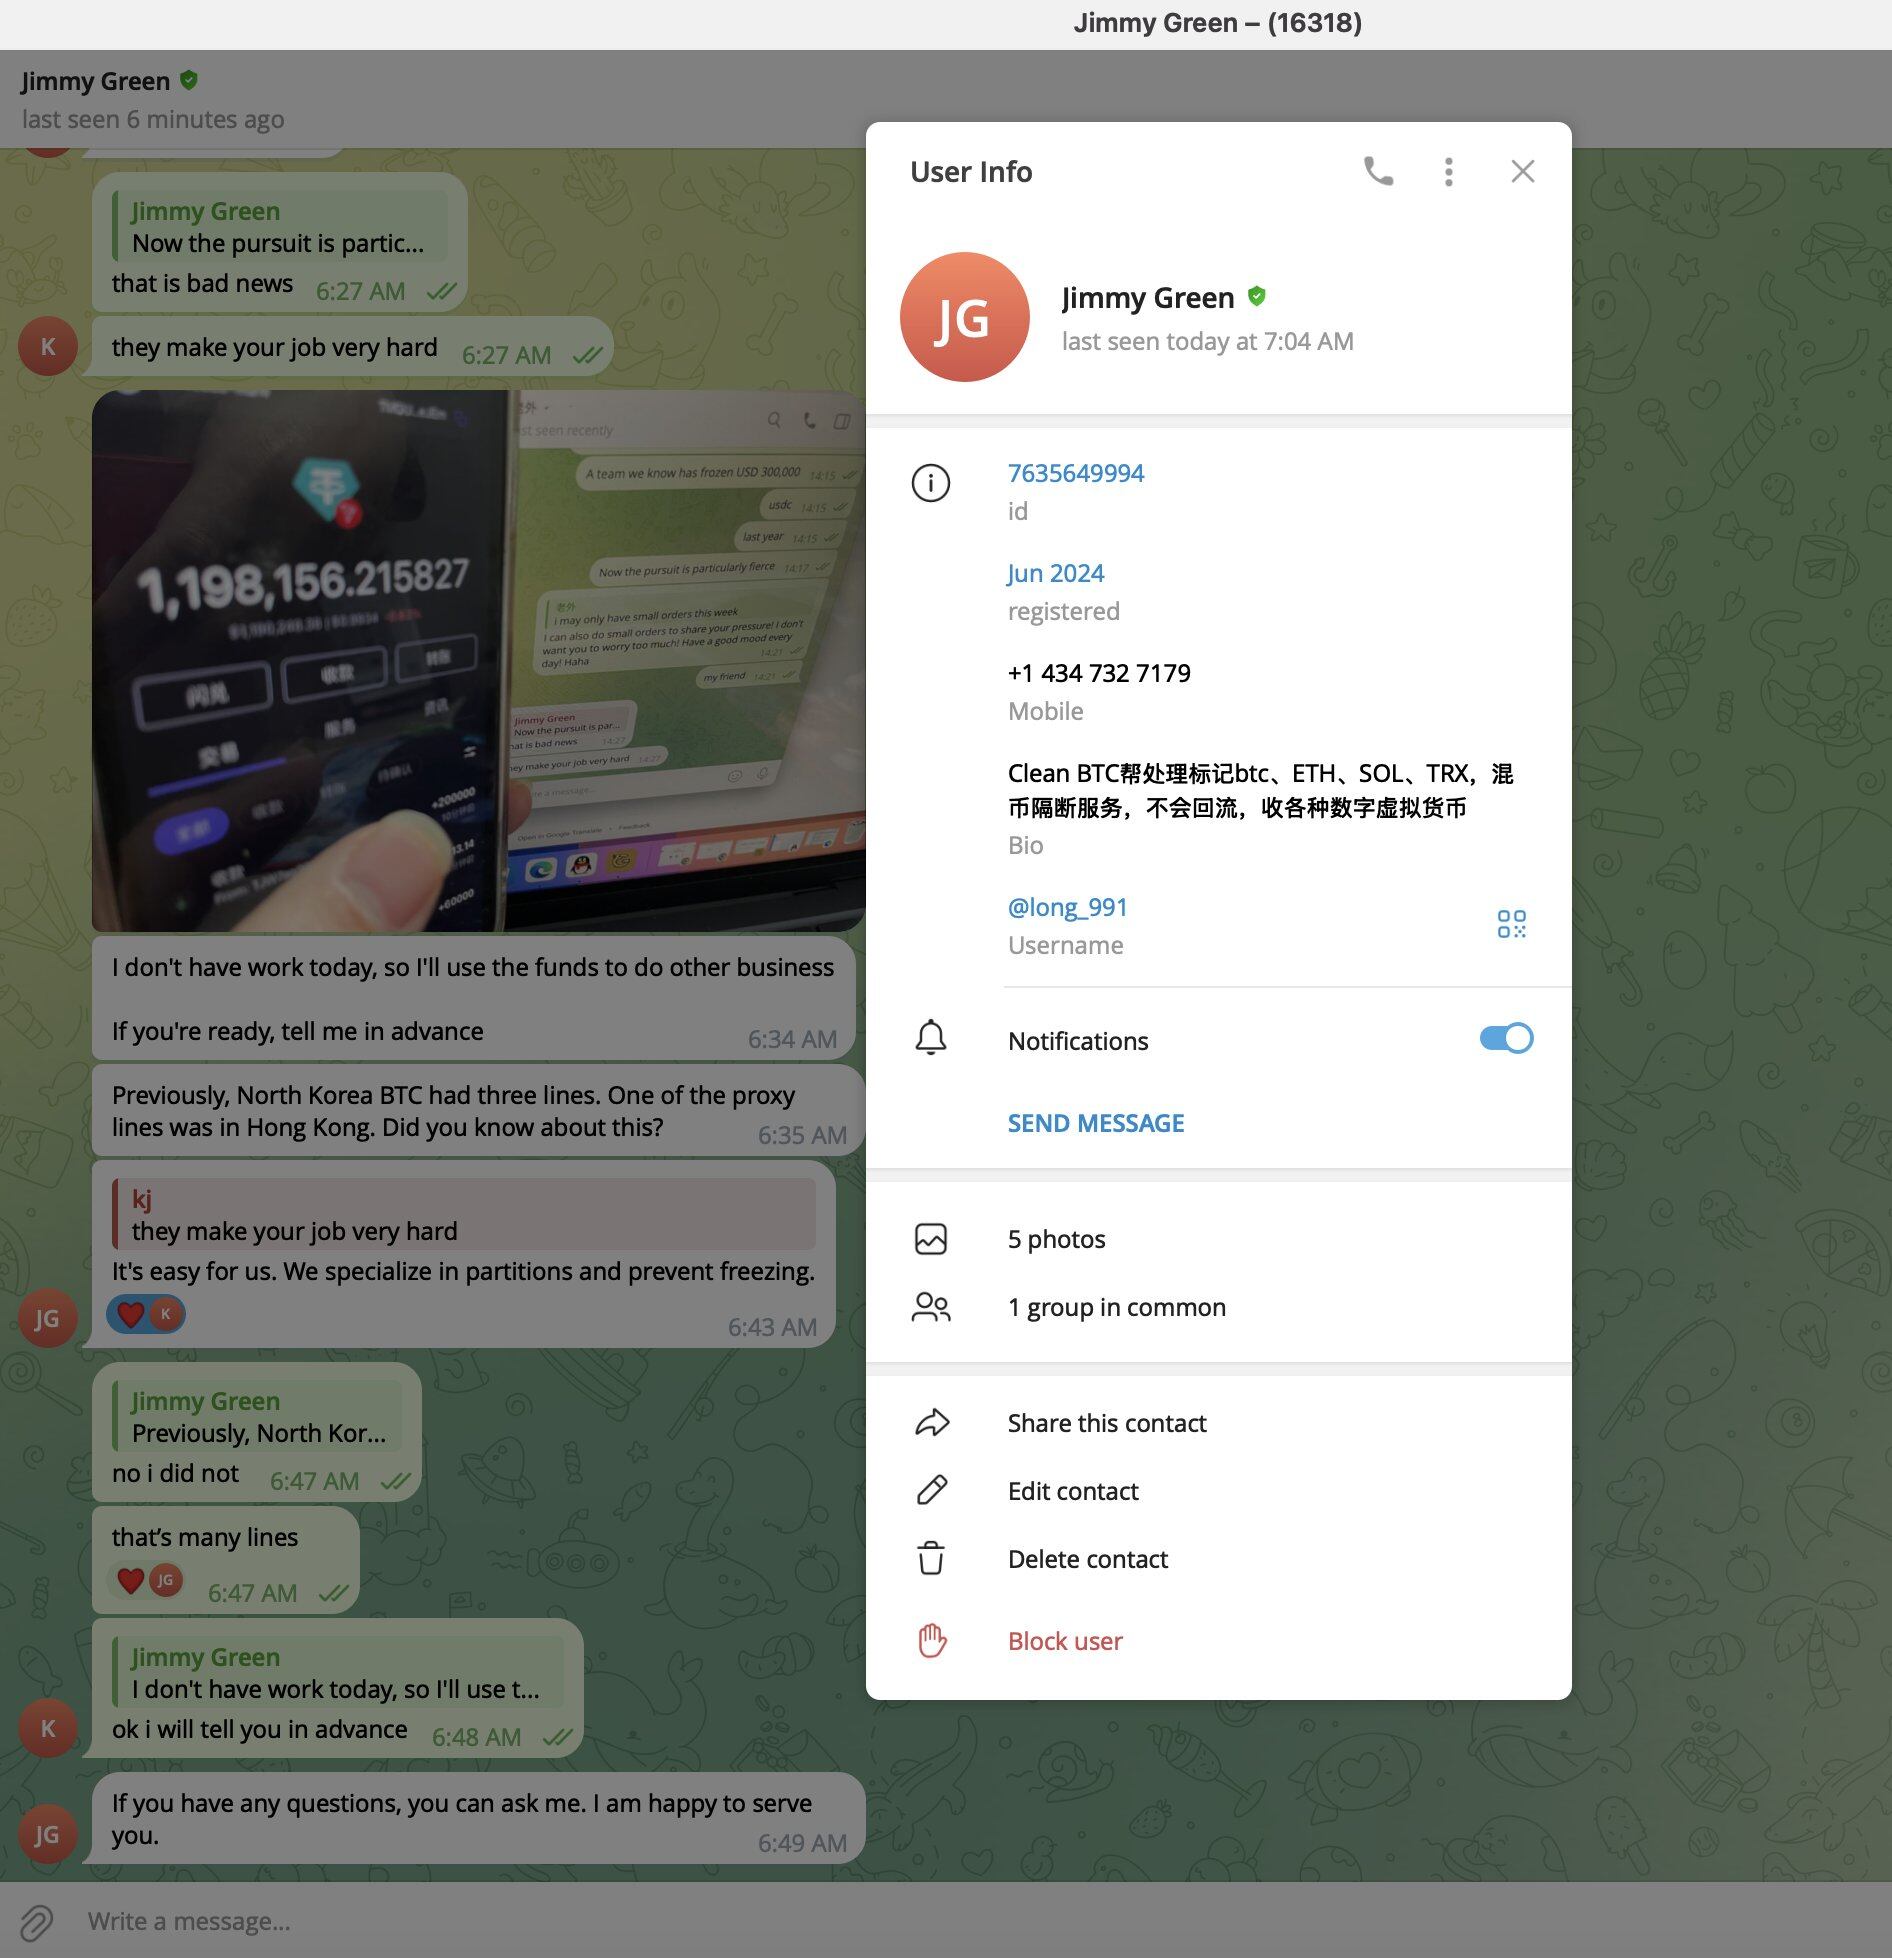
I began reaching out to these accounts, one of whom used the alias "Jimmy Green" on Telegram.
- Jimmy Green's Telegram username: long_991
- Jimmy Green's Telegram ID: 7635649994
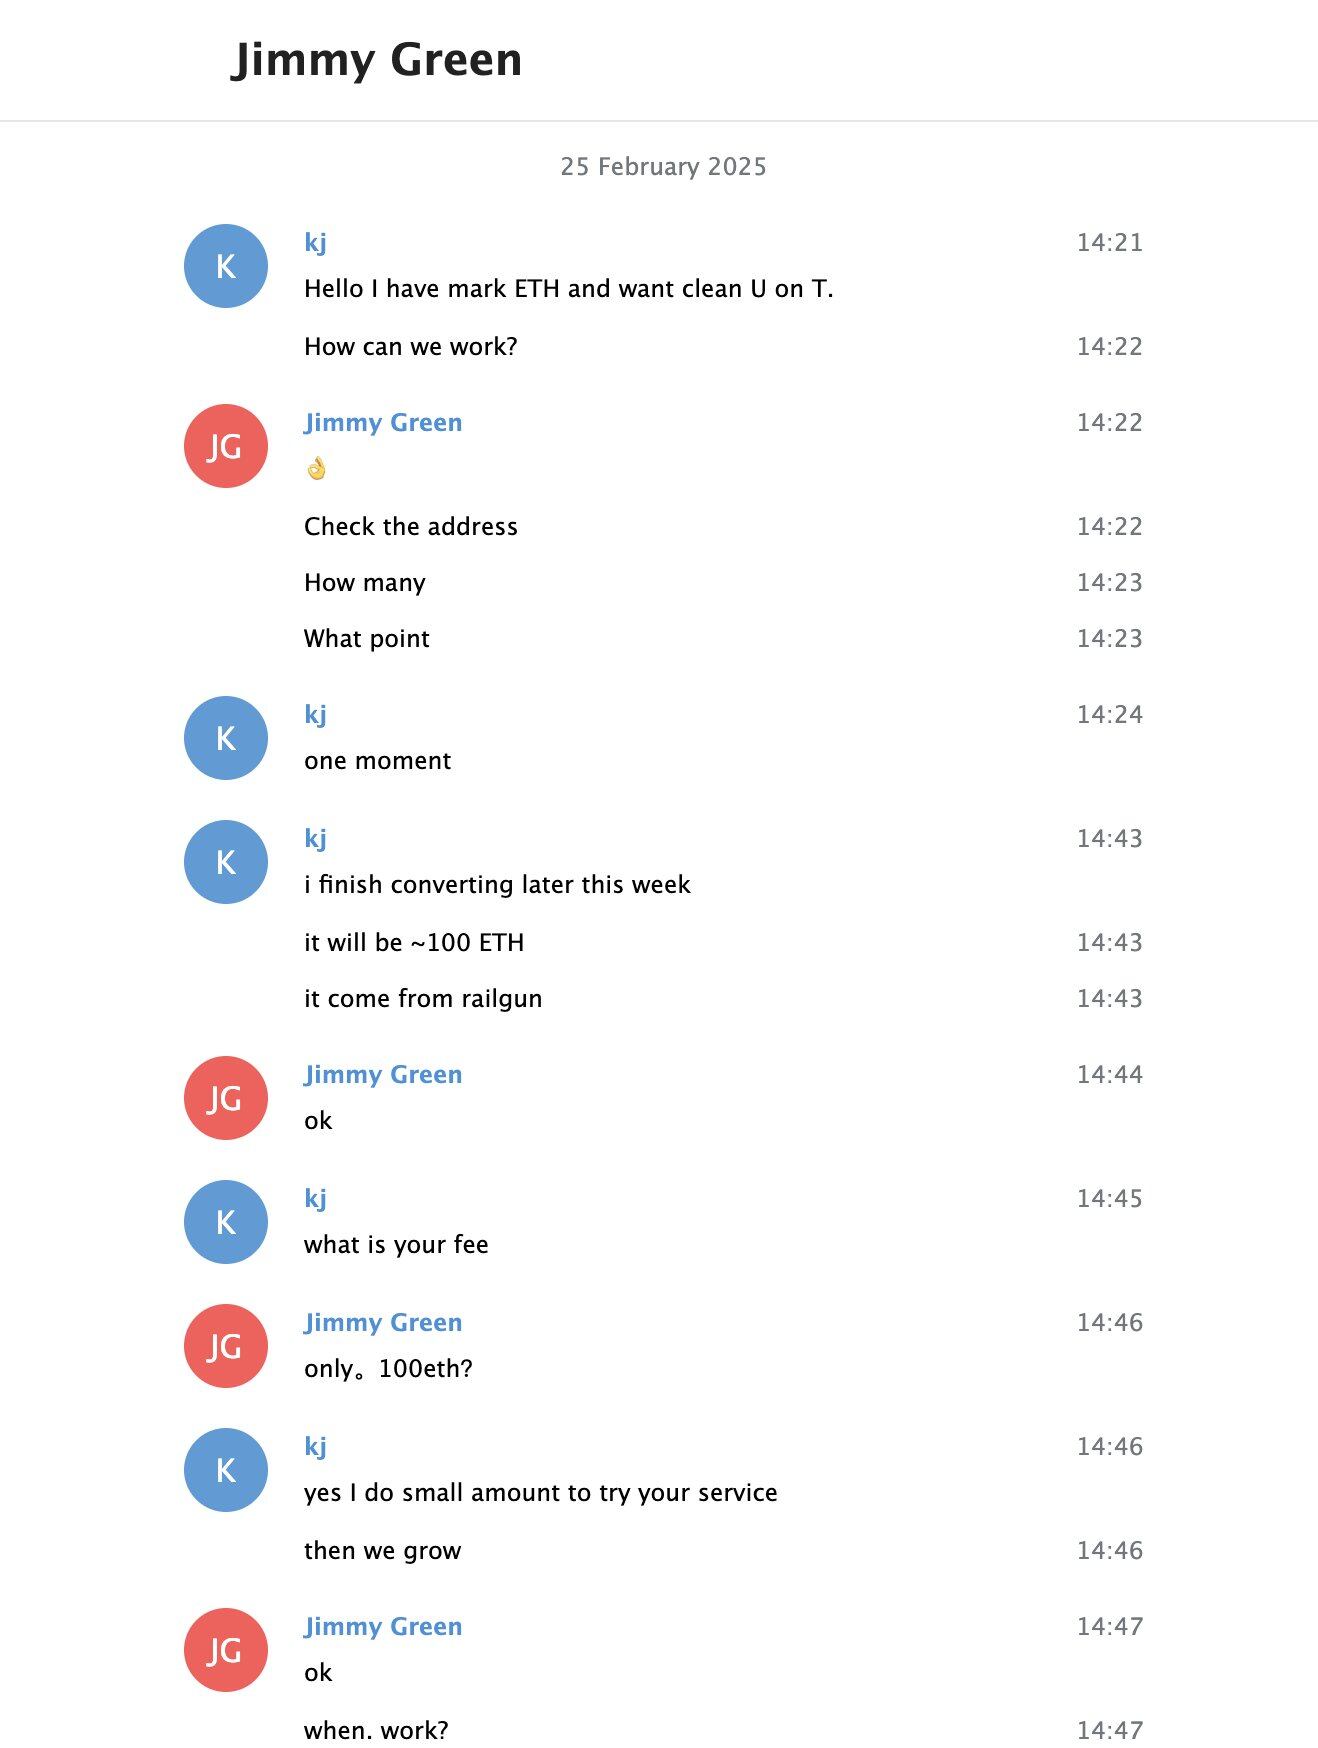
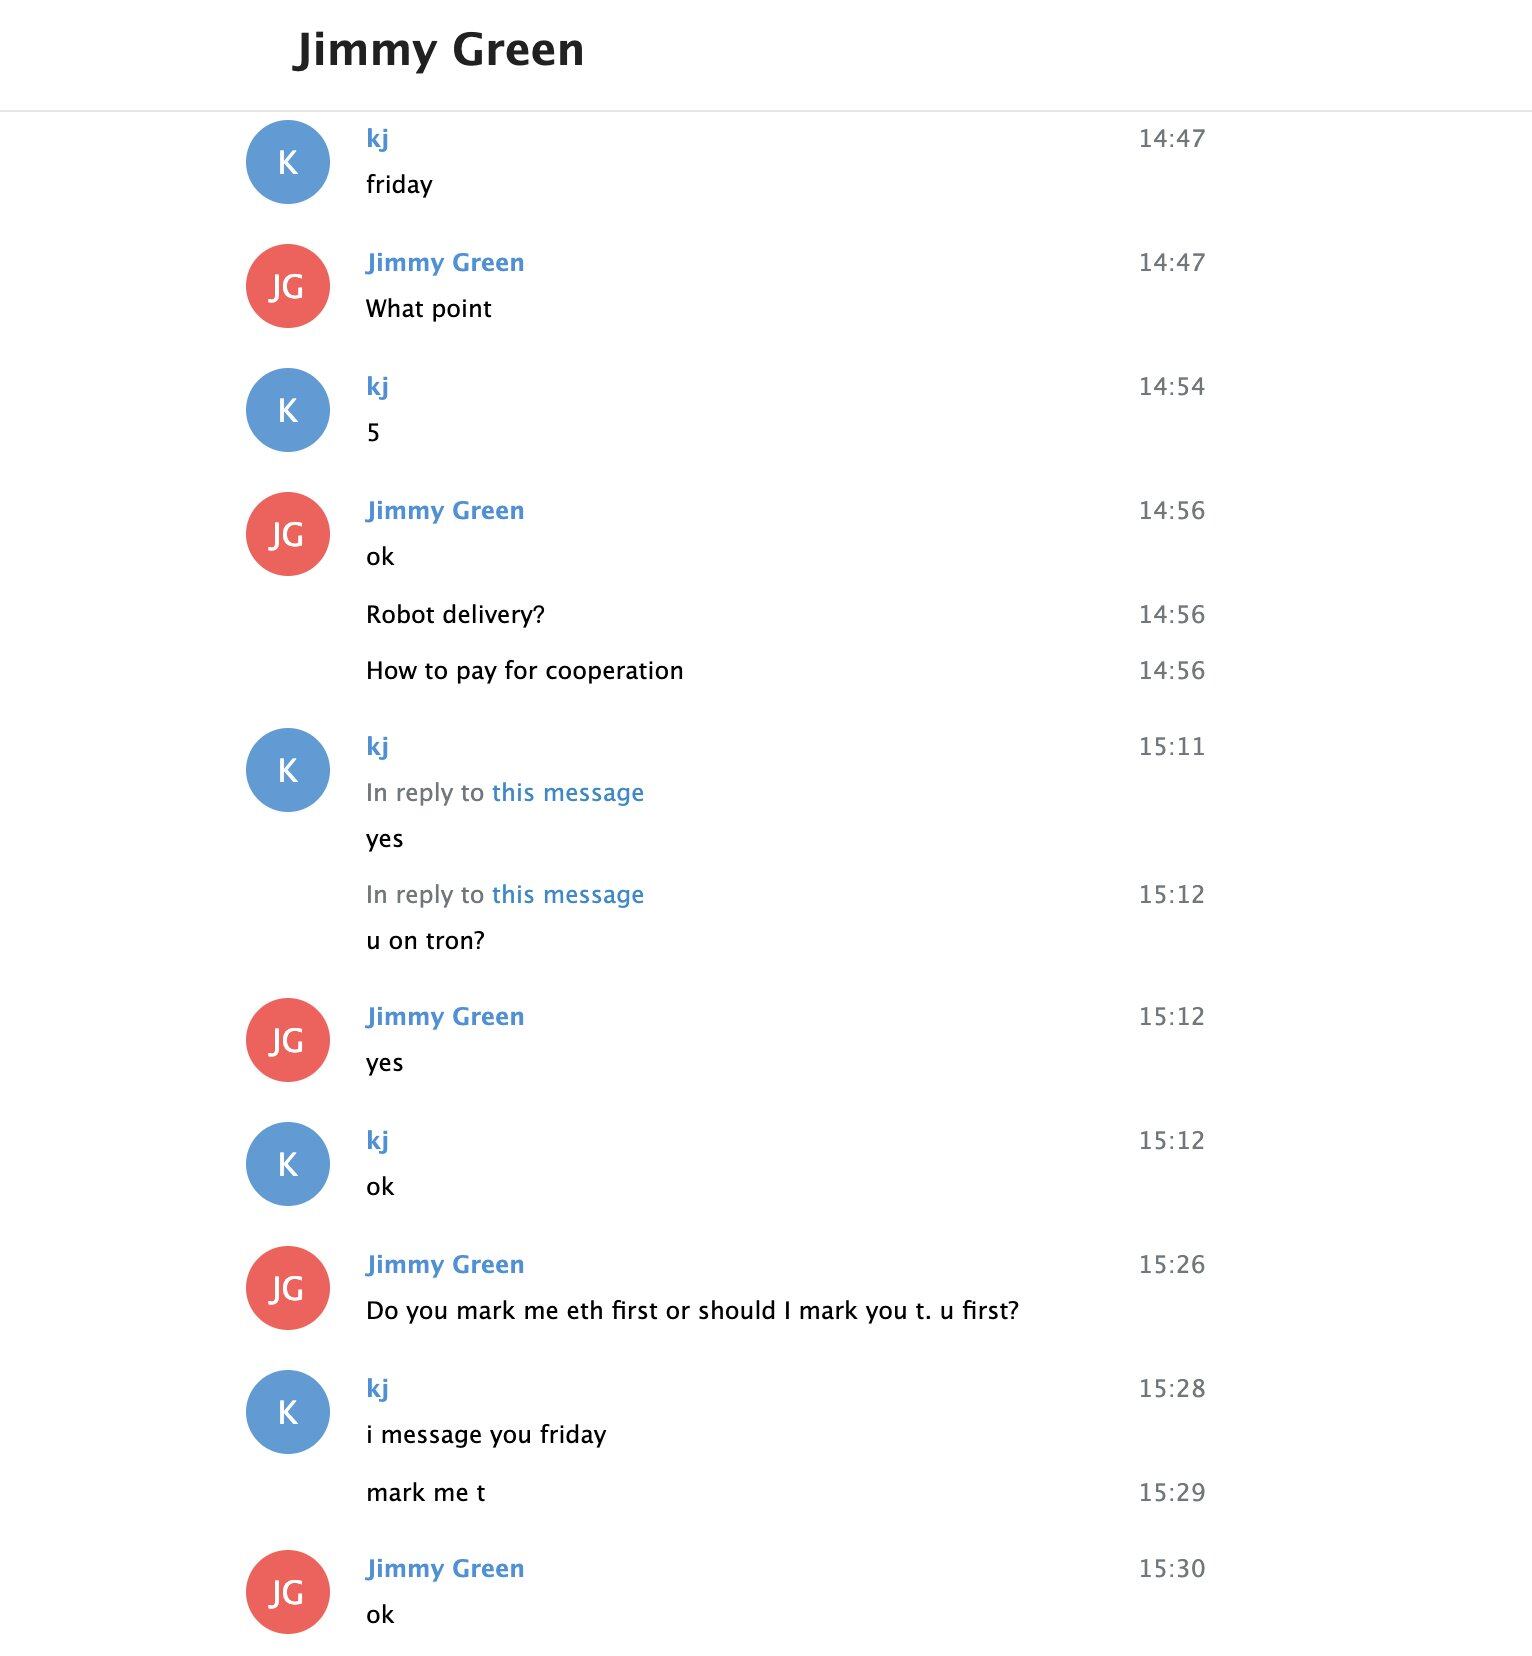
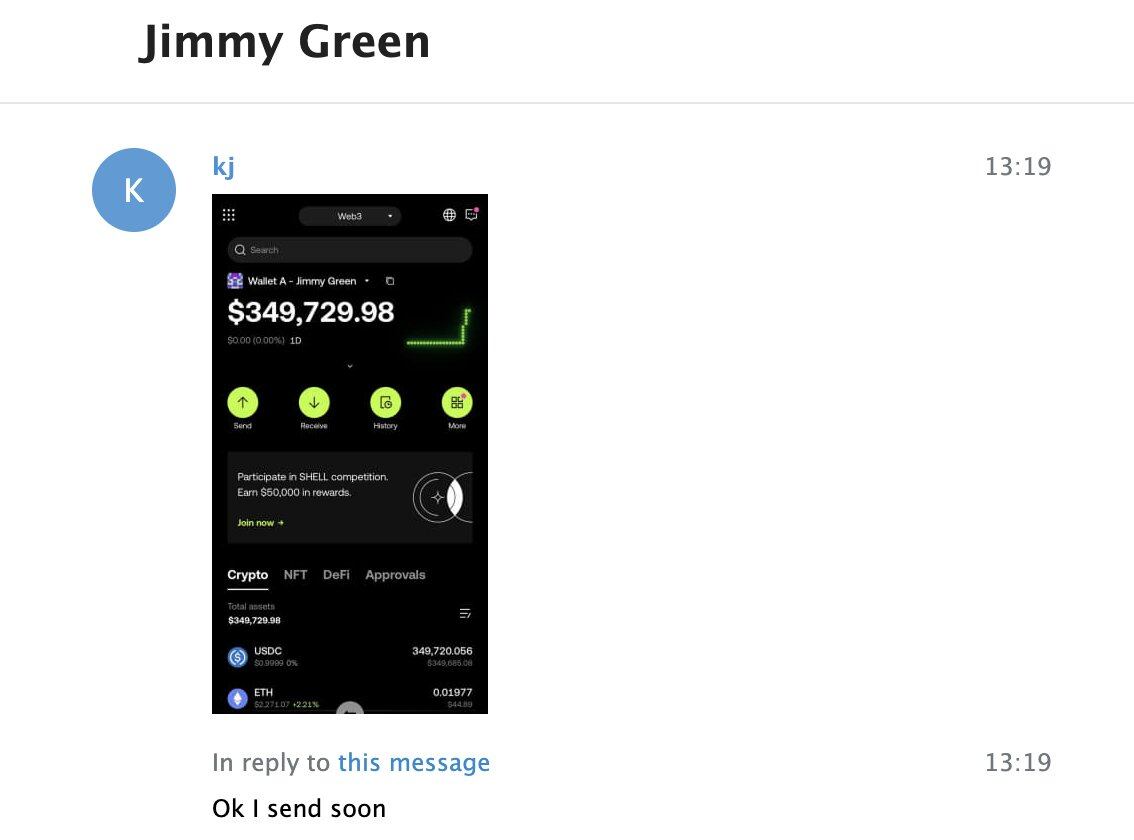
On March 6, 2025, I deposited $349,700 in USDC into a new address on Ethereum, preparing to conduct several transactions with Jimmy Green.
- My address: 0x073256b50d66a7eb005f2a504d0a4fb6ea62a276
Jimmy provided his address (starting with 0xbaa5) for me to send USDC to, in exchange for his USDT on the Tron chain.
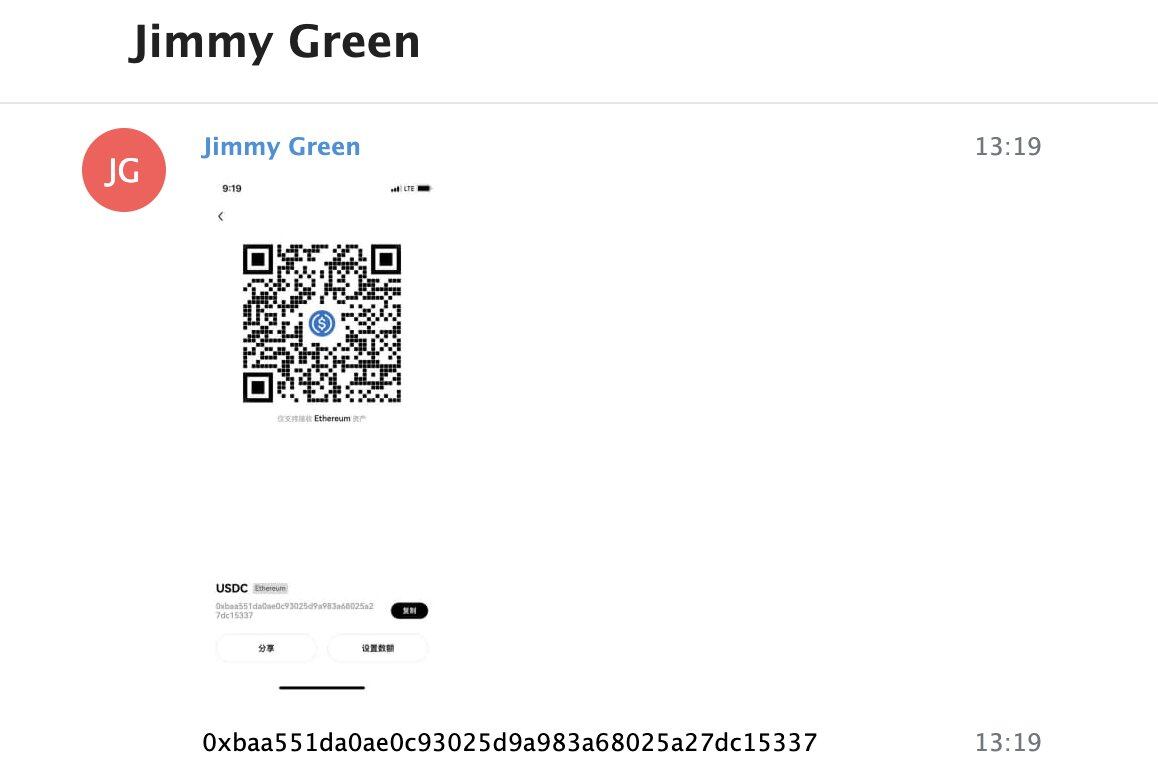
The gas fees for the address starting with 0xbaa5 were provided by another address starting with 0xbcb4, which can be directly traced back to the Bybit hacked funds and has been listed on the public blacklist website for the Bybit hack incident.
- Jimmy Green's Ethereum address: 0xbaa551da0ae0c93025d9a983a68025a27dc15337
- Jimmy Green's Tron address: TPwXAPwYaDCm7GrzNFiMmNnofrxEVURXRM

To gain trust, I completed several more transactions with him. Other addresses used by Jimmy Green are listed below.
- 0x1893ef01e700b1359280e11736d1b89fe97ed216
- TS5hY6mm6UsCLNdVDWnsRA69LuAwfdn158
- TMGjdFeBf9T6kGB9ZmLzeaAPYWBokuyTuS
After that, Jimmy began tipping me off in advance about their movements in transferring Bybit stolen funds for North Korea before the transfers took place, as well as basic details about their operations in Hong Kong and mainland China.
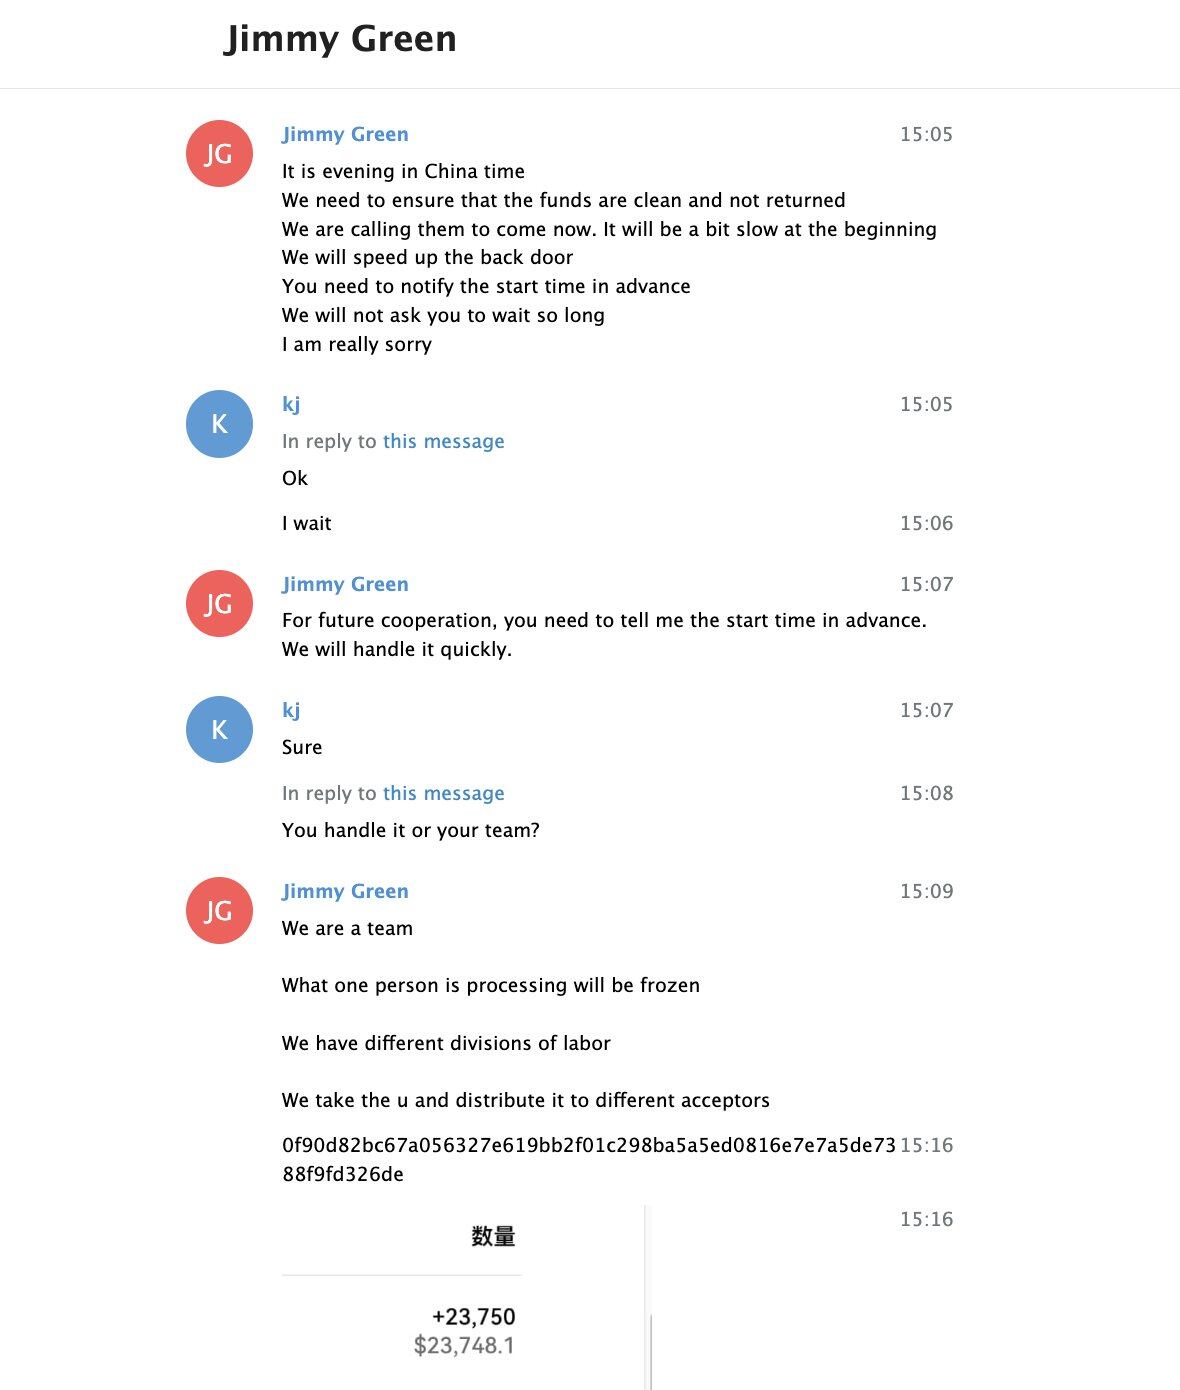
For example, he would reveal a day in advance that funds would be transferred to Solana, and the next day the transfer indeed occurred on-chain. He claimed his team helped launder the vast majority of the $1.5 billion stolen from Bybit, which perfectly matched the money laundering patterns I had observed.
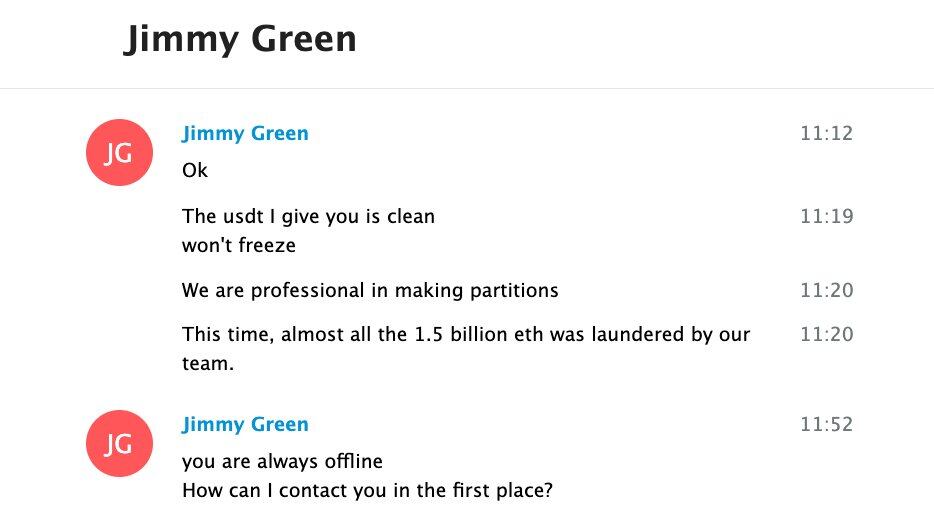
At this point I realized I had to keep trading despite a 5% loss on each order, gambling on obtaining as much actionable intelligence as possible, as quickly as possible.
In one case on March 12, 2025, Jimmy shared a screenshot of himself transferring funds cross-chain. By comparing the amounts and timestamps on the THORChain explorer, I successfully matched an order created just minutes after he sent the message.
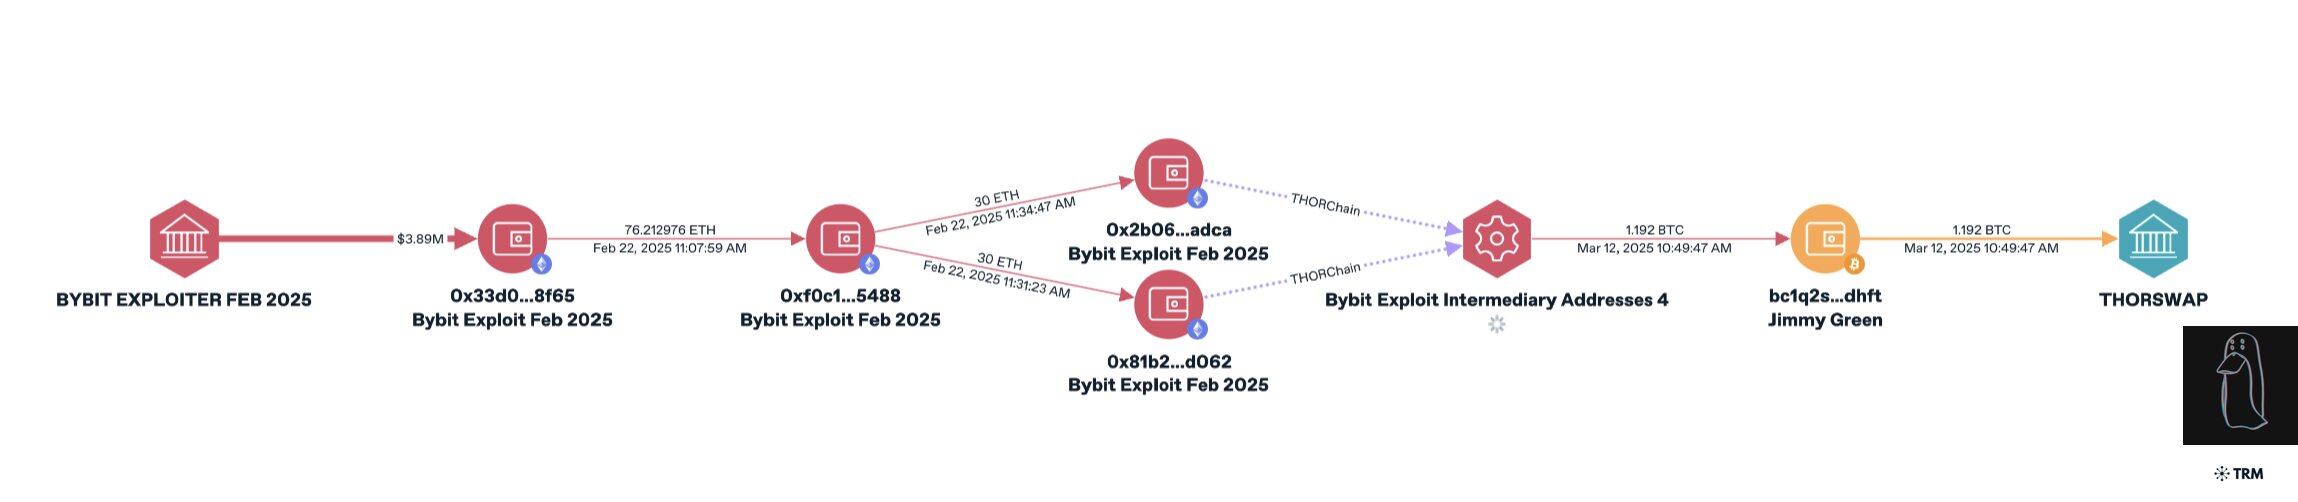
- Transaction hash: 81a85130b36057428e64b6f97215f77b5a197776a8f1b3a61c8cd0ee1ebfa8c1
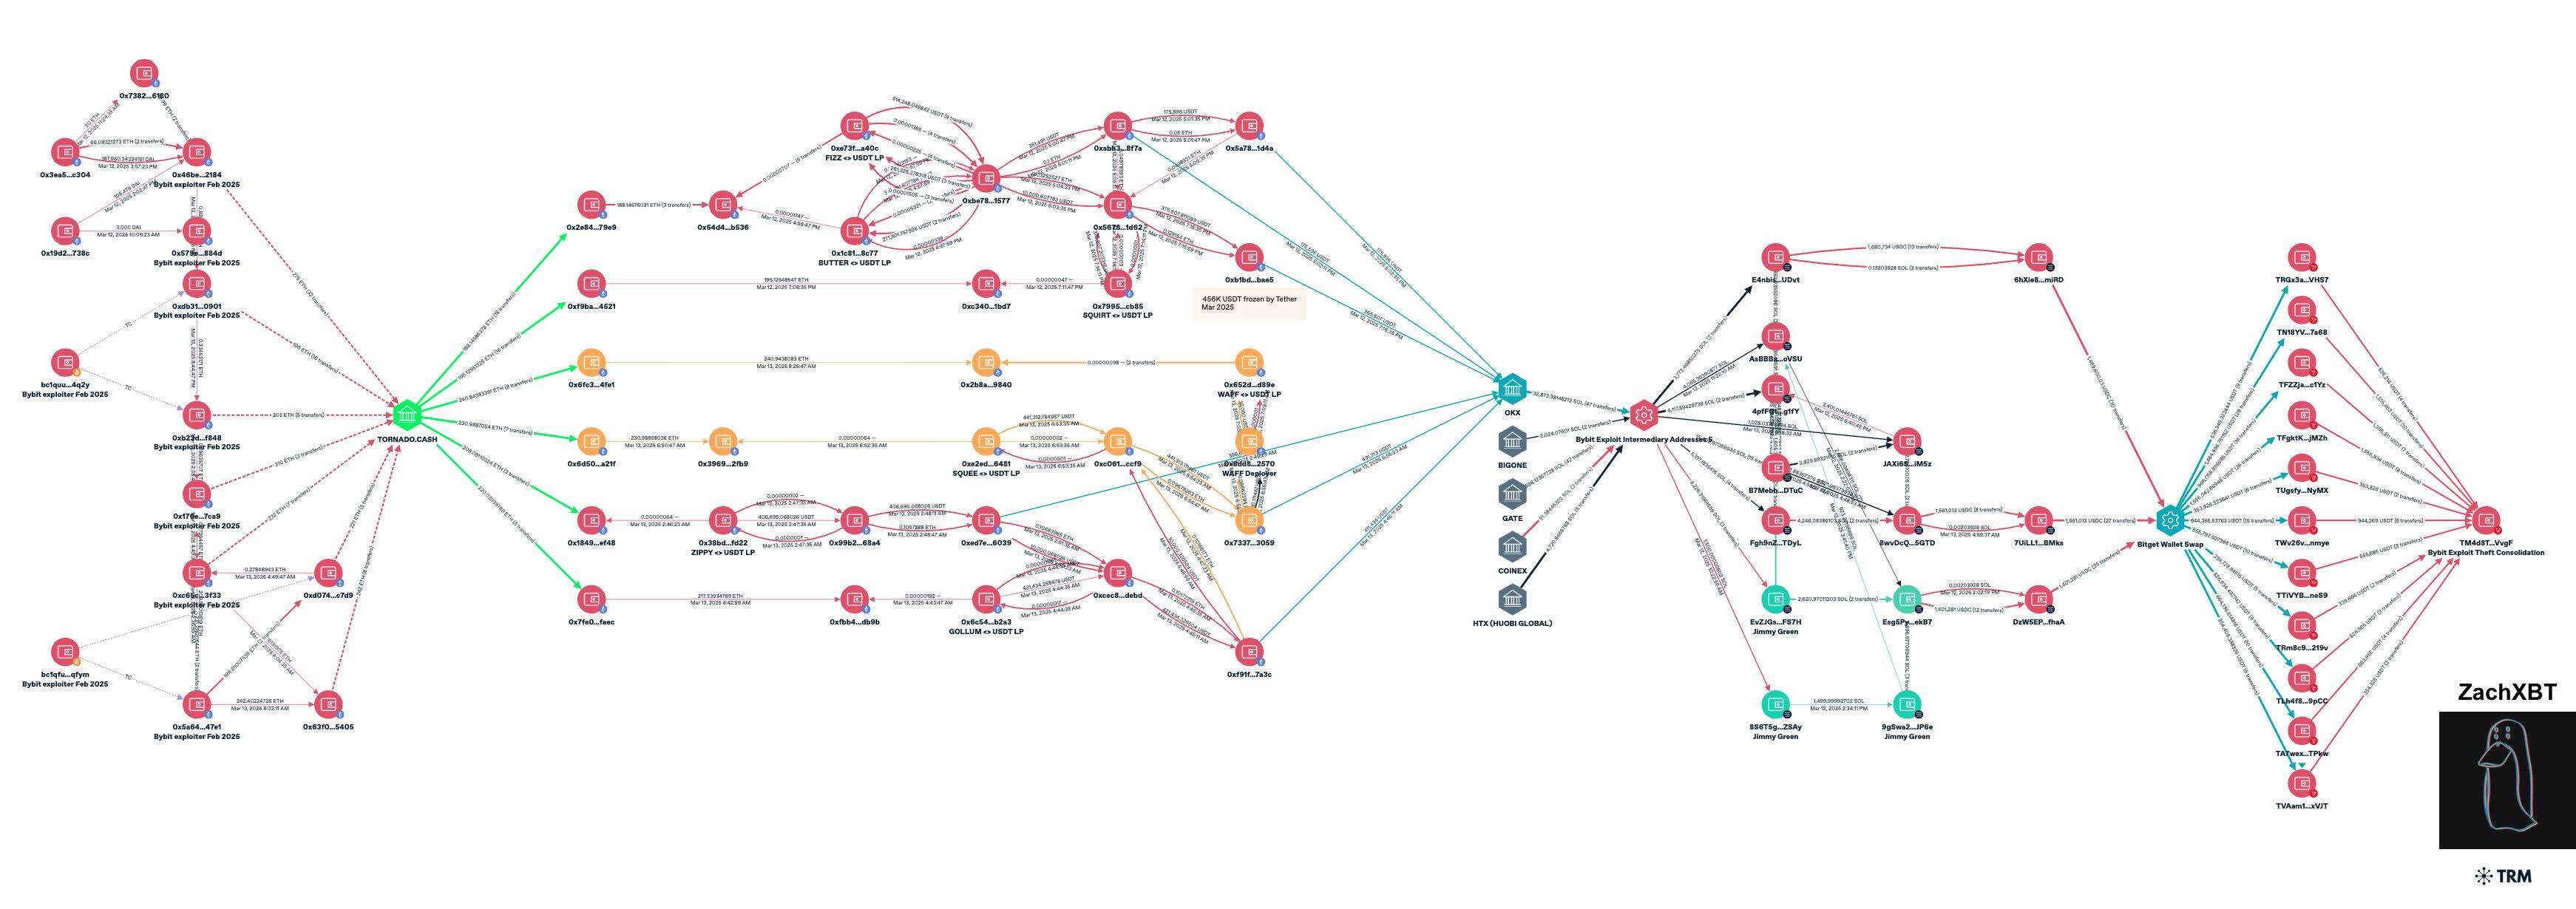
Jimmy also provided three Solana addresses (listed below), which revealed an address cluster linked to over $12 million in Bybit stolen funds, at the time being cross-chain swapped in real time through BTC ➡️ ETH ➡️ SOL ➡️ Tron.
- 9gSwa2Mew9P21Wxs8nFgDujTurKZx1nBEVRv6K5sJP6e
- EvZJGsDymrSUQyF23HLKEgUpjfd9XN1GTmm8AG6pFS7H
- 8S6T5gL2w5z4M9TCehMgQjxVm3Q6R7WDHp6WFfbtZSAy
Subsequently, $442,000 in USDT associated with this cluster was successfully frozen by Tether (0x652d7f9edaaa8891be2de74ea568d70af823d89e). The cluster also employed a novel money laundering technique: using illiquid tokens to launder money through Uniswap liquidity pools (LPs).
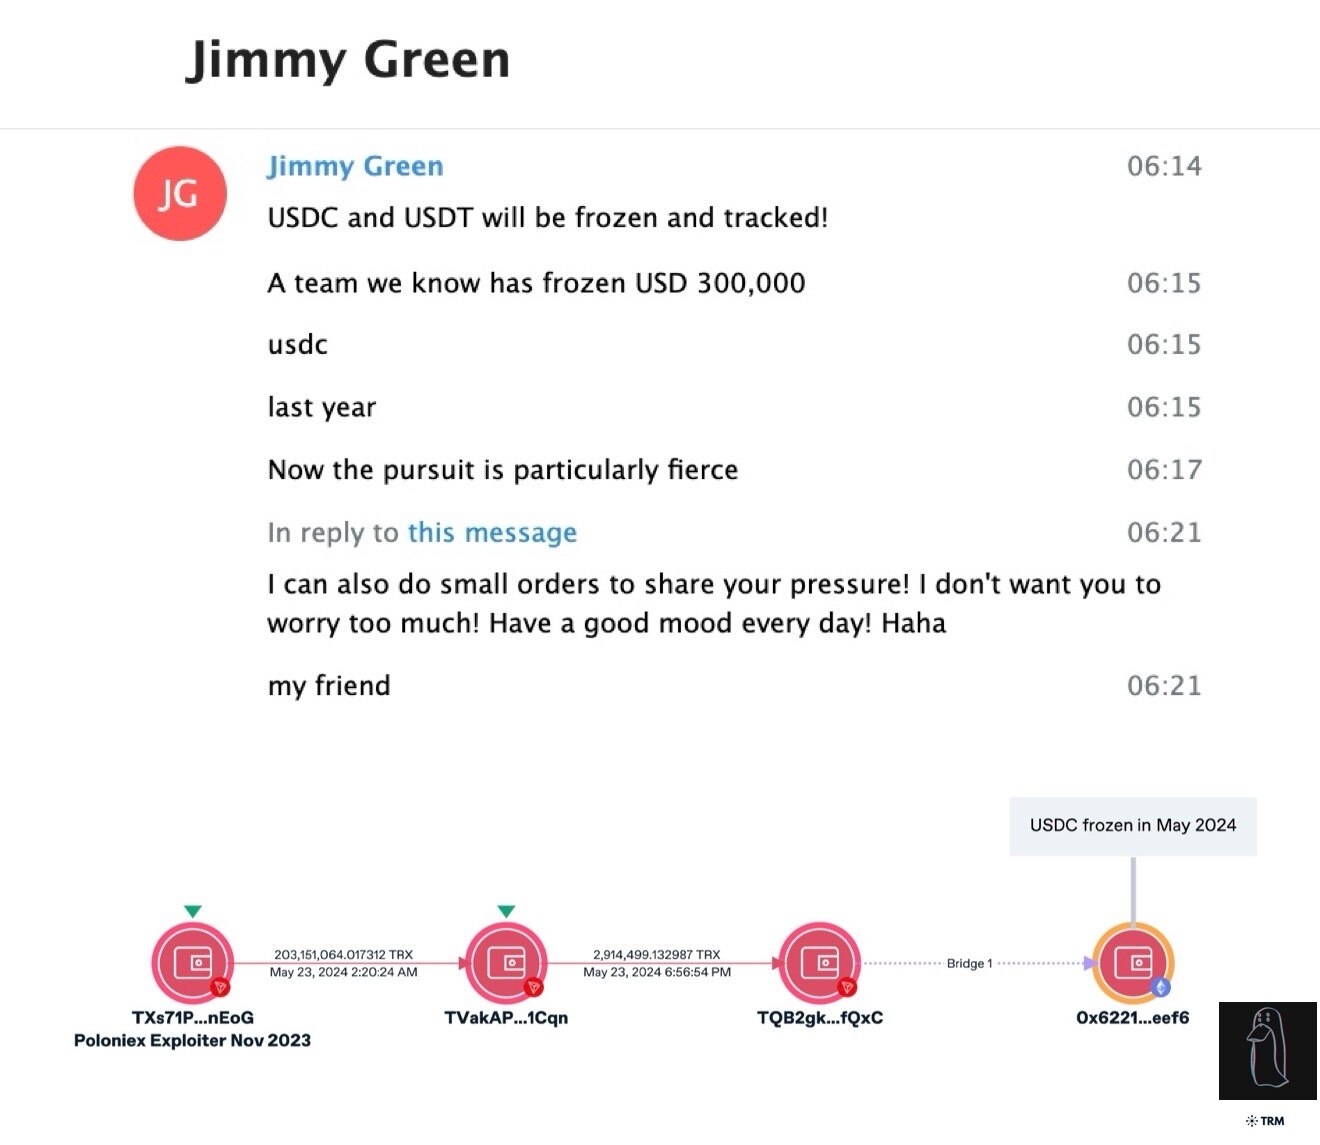
Jimmy once mentioned that a team he knew had about $300,000 frozen in 2024. I confirmed this freeze on-chain, with the actual amount being $332,000 in USDC originating from the Poloniex hack incident.
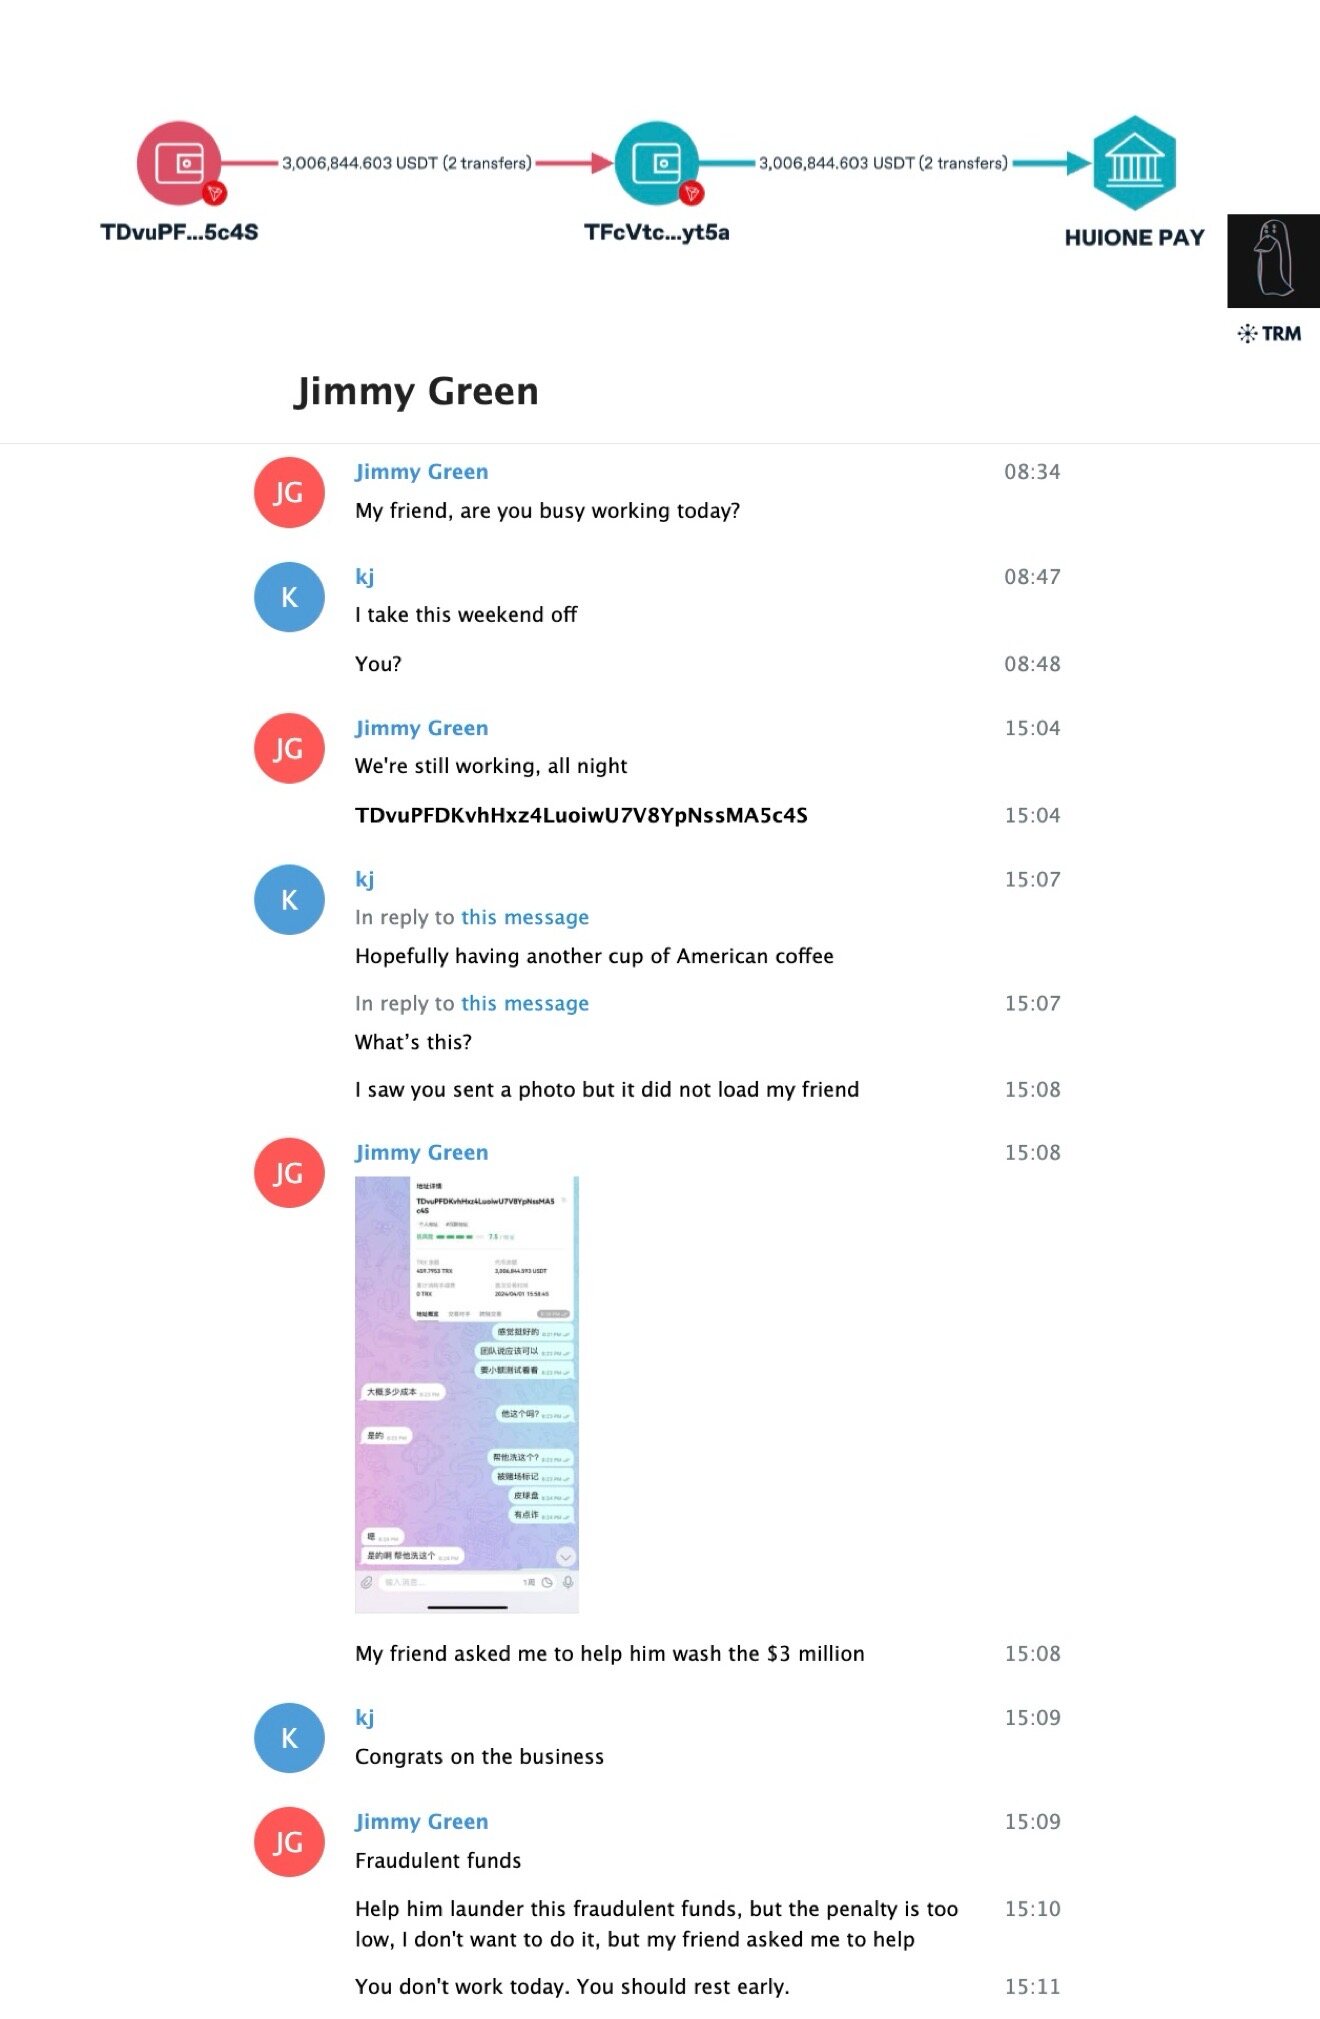
Jimmy also revealed that they had laundered $3 million in fraud proceeds for another client. I traced these funds to a hot wallet of Huione Guarantee, a platform that has now been sanctioned and whose former chairman has been arrested.
Throughout our communications, beyond discussing money laundering for North Korea, Jimmy and I also chatted extensively about everyday matters. He talked about playing mahjong, catching wild rabbits, food, diet meals, family life, and vacationing at Disney.
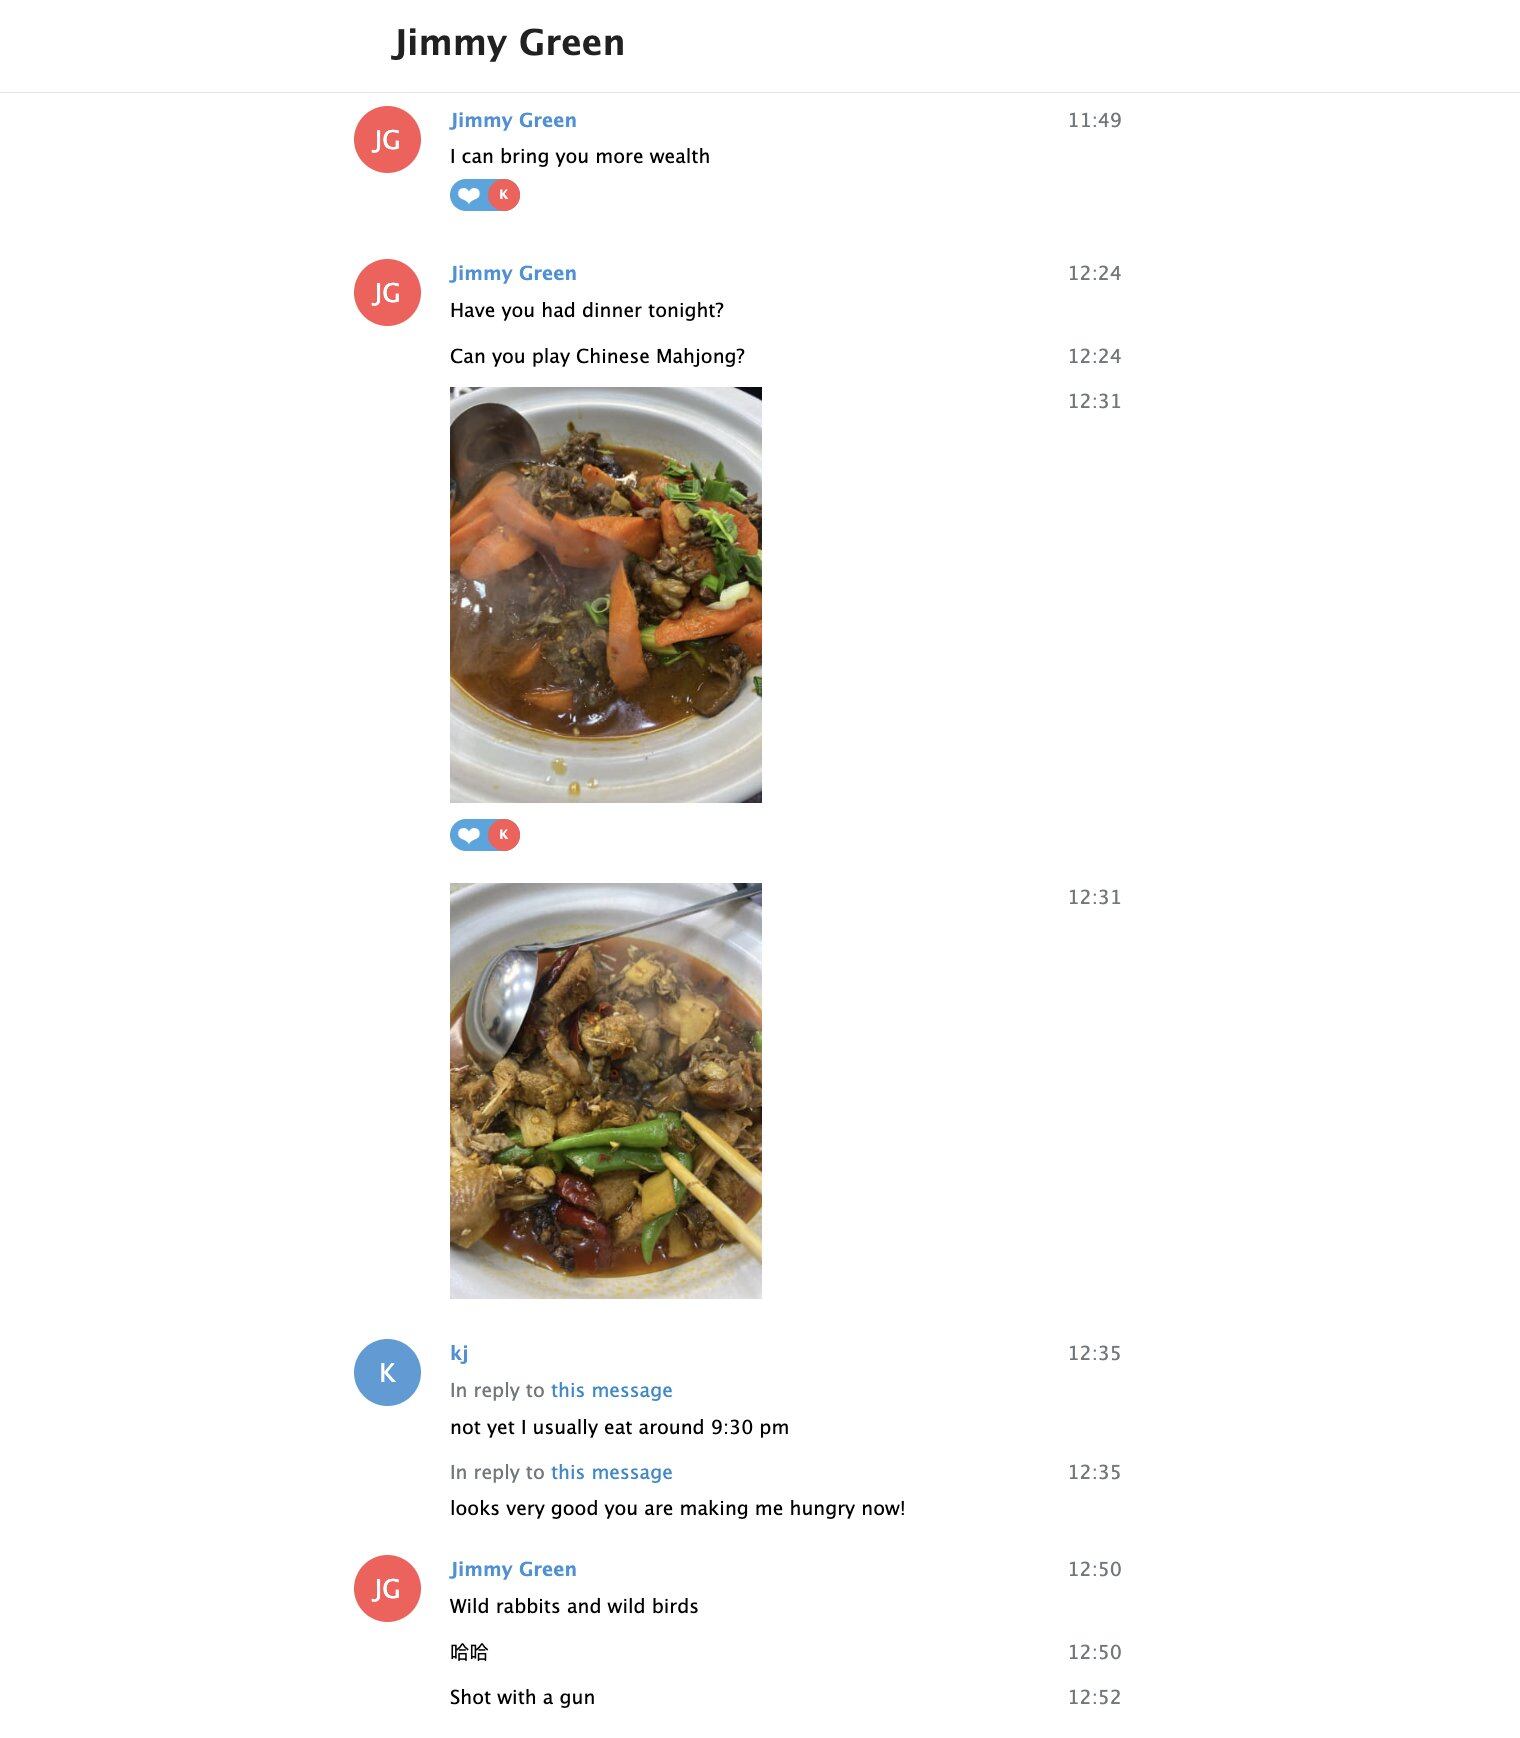
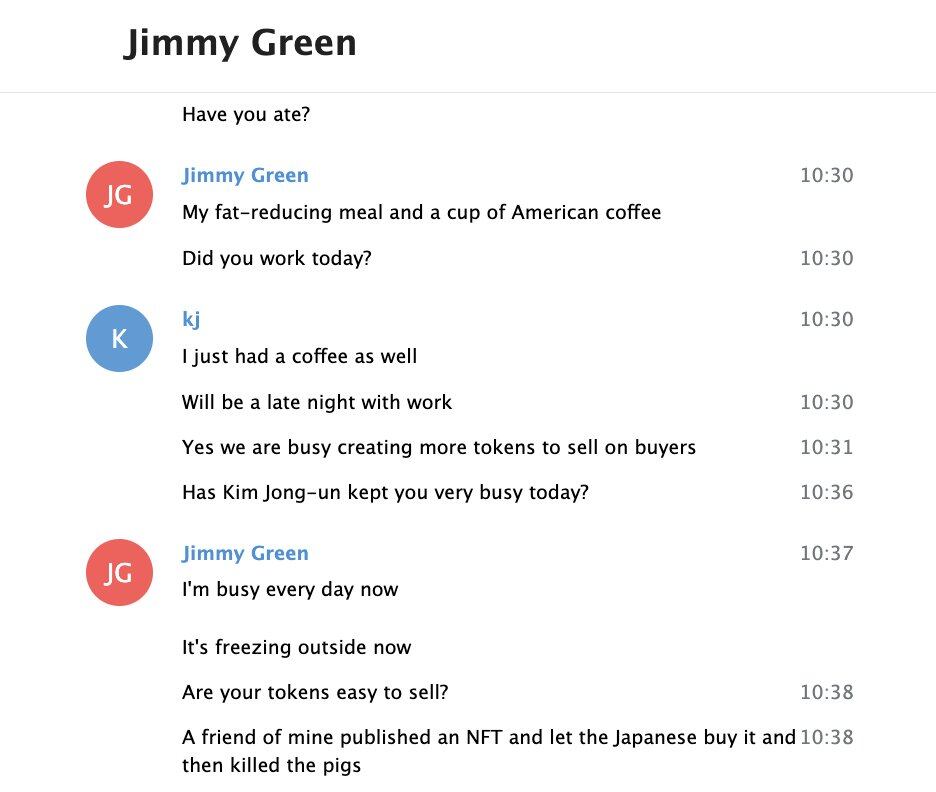
It's worth noting that his grammar was awkward, possibly because he was using translation software.
The reason I'm publishing this article is in the hope of continuing to receive grants or donations from foundations or individuals, as this allows me to take on higher risks to investigate special cases that others might consider unfeasible or too costly.
In this case, I fronted $349,700 of my own capital, took a 5% loss on every order, and bore the risk of Jimmy absconding with the funds at any moment, as well as the unknown physical danger of dealing directly with a criminal syndicate.
Since 2022, I have helped freeze over $75 million in funds related to North Korean hacking incidents. My investigative findings have been shared immediately with trusted private-sector investigators and the law enforcement agencies handling this case.
Due to the highly sensitive nature of the investigation, I was previously unable to disclose these details earlier. This is also a frustrating aspect of my work: I can't always publish investigation results as promptly as I'd like, and I currently have a backlog of significant findings from other cases.
If this case resonates with you and you're able to offer support, please feel free to reach out to me.